Clear Ownership by Control
Assign legal, engineering, and operations ownership for every checklist item.
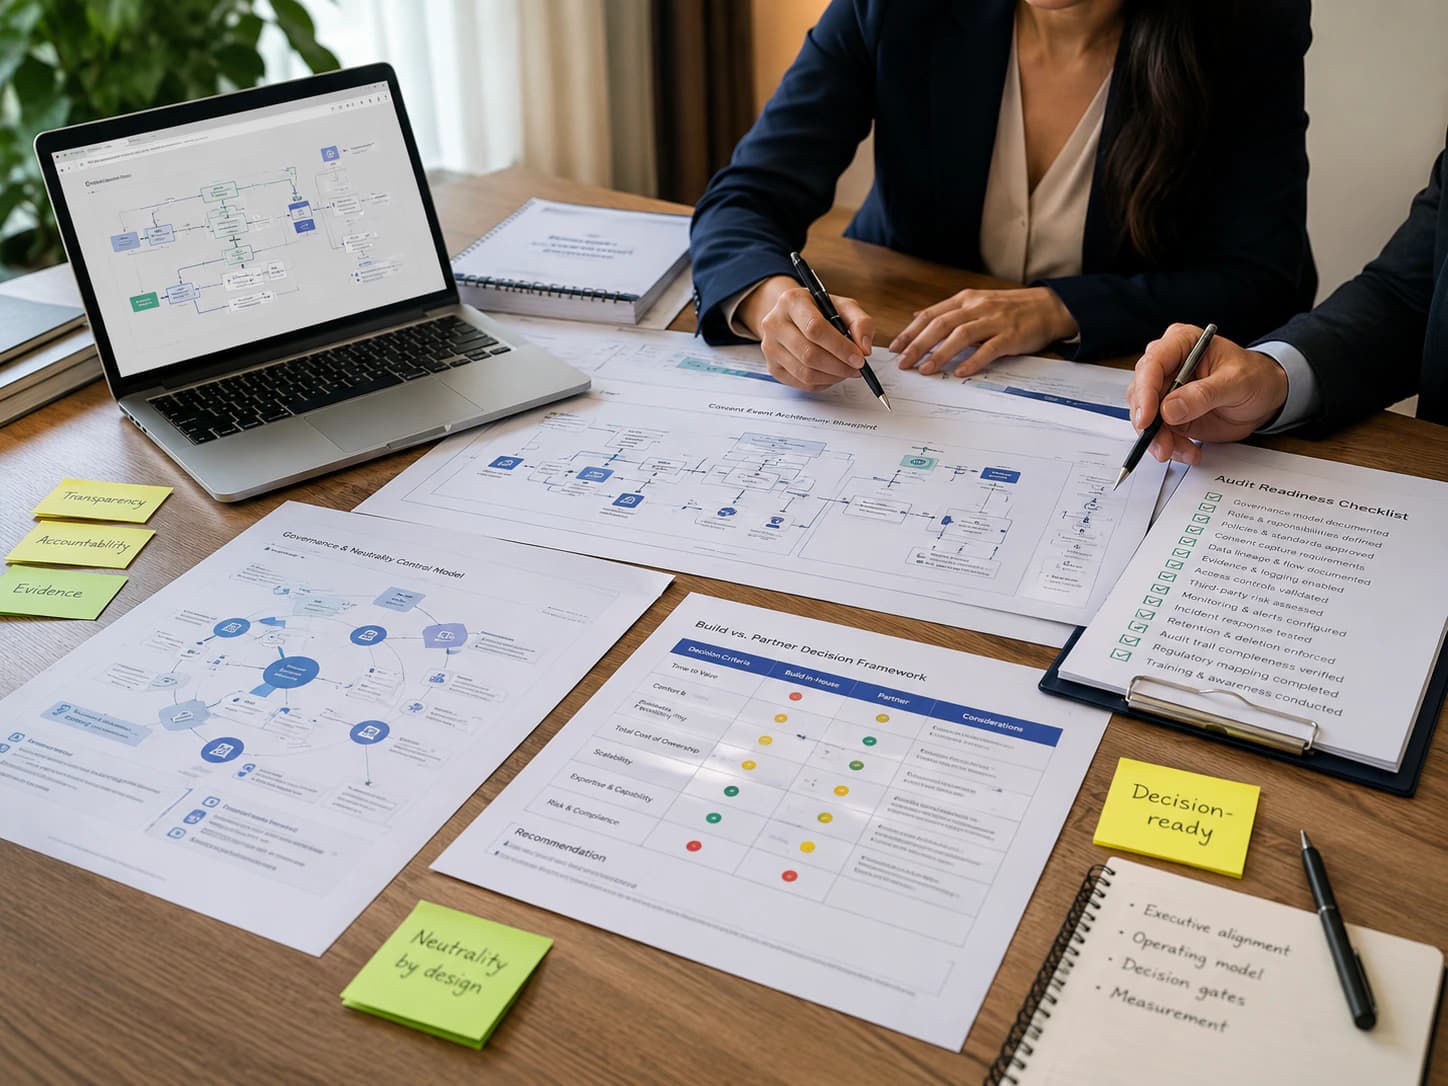
A working checklist that translates legal obligations into owned controls, engineering tasks, and audit evidence.
Most DPDP checklists fail because they stop at legal text. This framework is built for delivery teams with owner mapping, build tasks, test steps, and evidence requirements.
Best for teams that need to move from policy drafts to measurable implementation progress in the next 60-90 days.
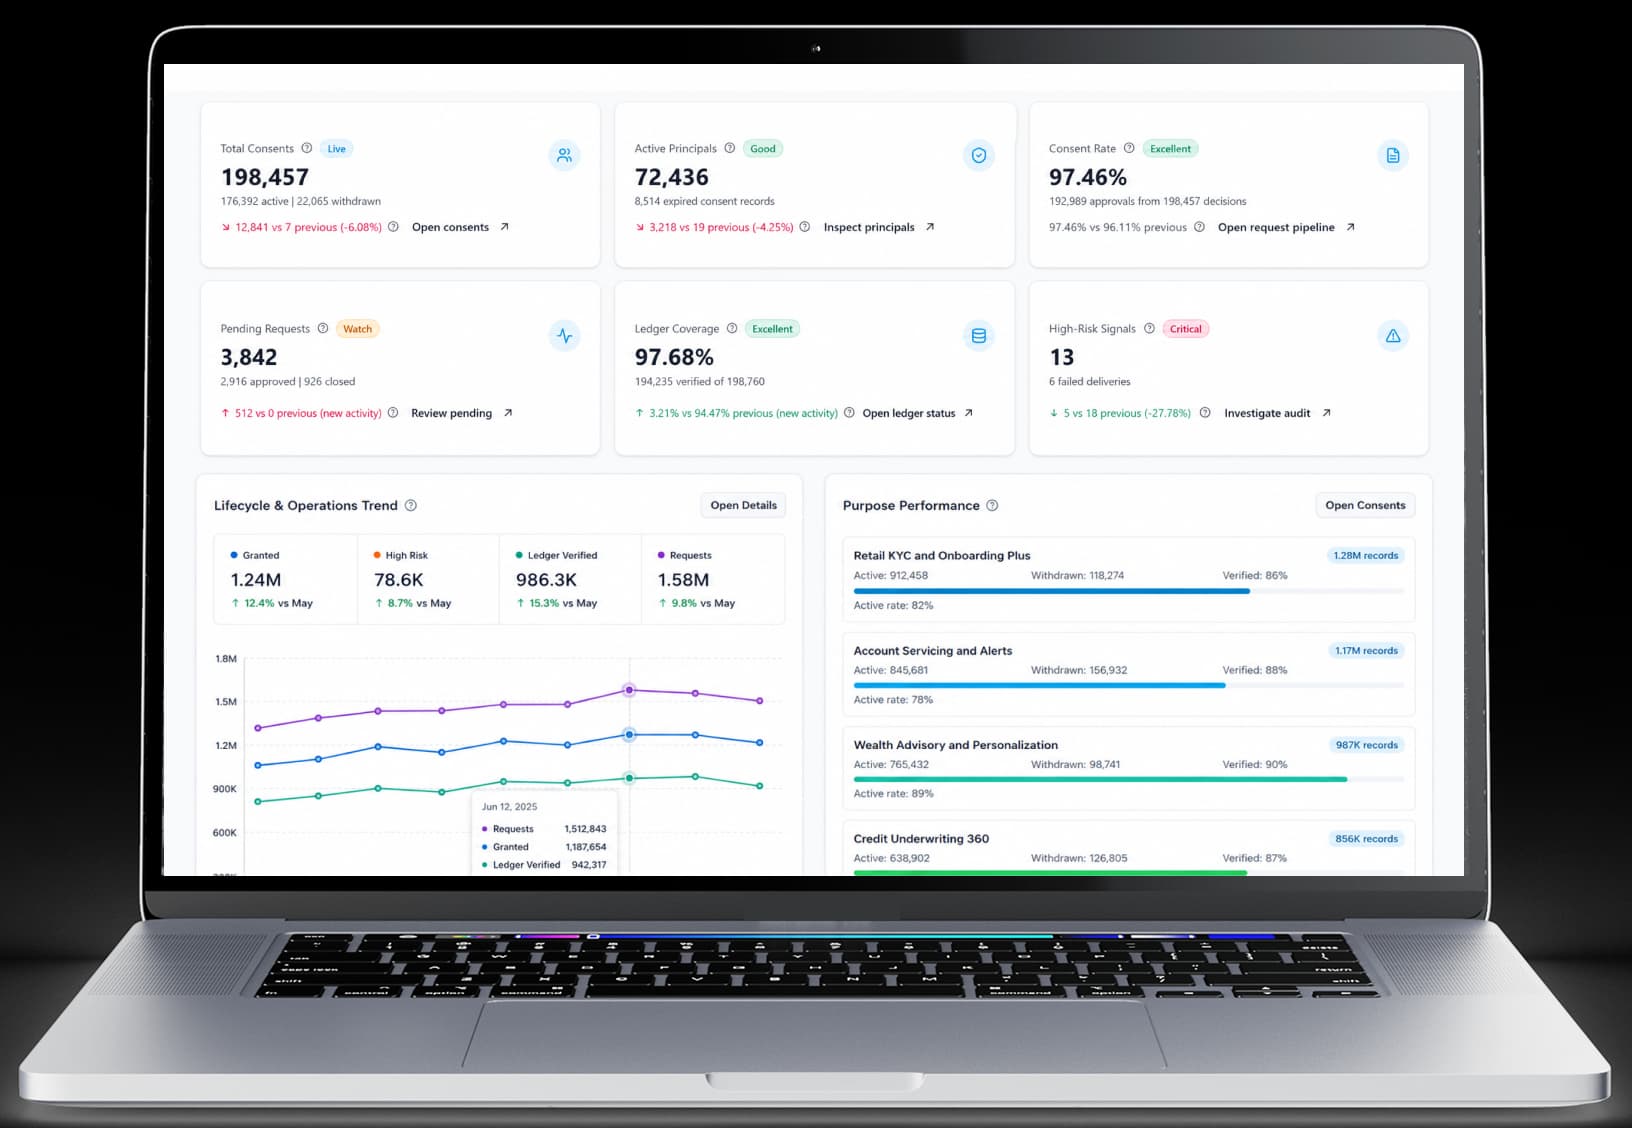
At A Glance
Evidence Focus
The Digital Personal Data Protection Act lays out a set of obligations for every business that collects personal data in India. A compliance checklist translates those legal obligations into concrete tasks that your legal, product, and engineering teams can actually execute.
Most checklists you find online are high-level summaries of the law. They tell you what the act says, but not what to build, who owns each task, or what evidence you need for an audit. That gap between legal text and operational delivery is where most teams get stuck.
 01 / 03
Short answer: a useful checklist assigns owners, maps implementation tasks, tracks test status, and links each control to auditable evidence.
Each outcome maps to execution, ownership, and proof — not abstract policy language.
Most delays come from operating-model gaps, not tooling gaps. Teams move faster when ownership, policy, architecture, and evidence align before implementation begins.
Teams check boxes at policy level but do not know whether controls are truly live in systems.
Legal, engineering, and operations each assume the other team owns execution and follow-through.
Audit artifacts are compiled at the last moment instead of captured continuously during implementation.
Critical controls and low-risk controls are treated equally, slowing readiness and increasing risk.
Bring legal, DPO, engineering, and programme owners into one execution model with clear control ownership and evidence.
Teams coordinating DPDP readiness across legal, technical, and operational workstreams.
Move from control scoping to audit-pack readiness through a focused, evidence-led delivery path.
Mandatory controls mapped and ranked by enforcement and operational risk.
Map business processing realities against legal obligations and assign a risk score to each control.
Define implementation tasks, integration dependencies, and operational guardrails by owner.
Run legal, engineering, and operations workstreams together with weekly control reviews.
Run mock audits and collect evidence continuously before external scrutiny.
Align legal, DPO, engineering, and programme teams around the checklist outcomes each group owns.
Without a unified operating model
Checklist depth
Policy-level lists with limited execution detail
Ownership framework
Diffuse ownership and slower remediation
Audit preparedness
Ad-hoc evidence collection near deadlines
AquaConsento operating model
Checklist depth
Control-level implementation + evidence mapping
Ownership framework
Explicit legal-tech-ops accountability
Audit preparedness
Mock-audit aligned readiness scoring
Get practical answers about checklist ownership, implementation scope, review cadence, and audit evidence before planning the next step.
A DPDP compliance checklist is a practical control framework that helps organizations translate India's Digital Personal Data Protection Act requirements into owned tasks, technical controls, evidence artifacts, and review checkpoints. A useful checklist should not stop at legal obligations; it should show who owns each control, what needs to be implemented, and how proof will be maintained.
Use these linked pages together to cover strategy, controls, implementation, and evidence.
September 2026 · 6 min read
September 2026 · 6 min read