Operational Compliance Architecture
Use data privacy compliance software to unify control execution across teams, systems, and third-party processors.
Implement compliance software that supports governance, engineering workflows, and regulator-facing evidence. DPDP software is not a consent dashboard. It should connect user consent management, rights requests, processor governance, and audit evidence in one operating system.
Best for enterprises replacing fragmented compliance tools with a single execution and evidence system.
DPDP compliance software is not a single tool — it is an operating layer that helps teams execute DPDP Act compliance by connecting consent management, rights handling, processor governance, and audit evidence generation into one system.
Many teams start with spreadsheets and manual processes, which works until you have thousands of consent records, multiple data processors, and a regulator asking for evidence within days. At that point, you need software that enforces rules automatically and produces proof as a byproduct of normal operations.
 01 / 03
No. Software accelerates execution, but governance ownership and operating discipline remain mandatory.
Each outcome maps to execution, ownership, and proof — not abstract policy language.
Use data privacy compliance software to unify control execution across teams, systems, and third-party processors.
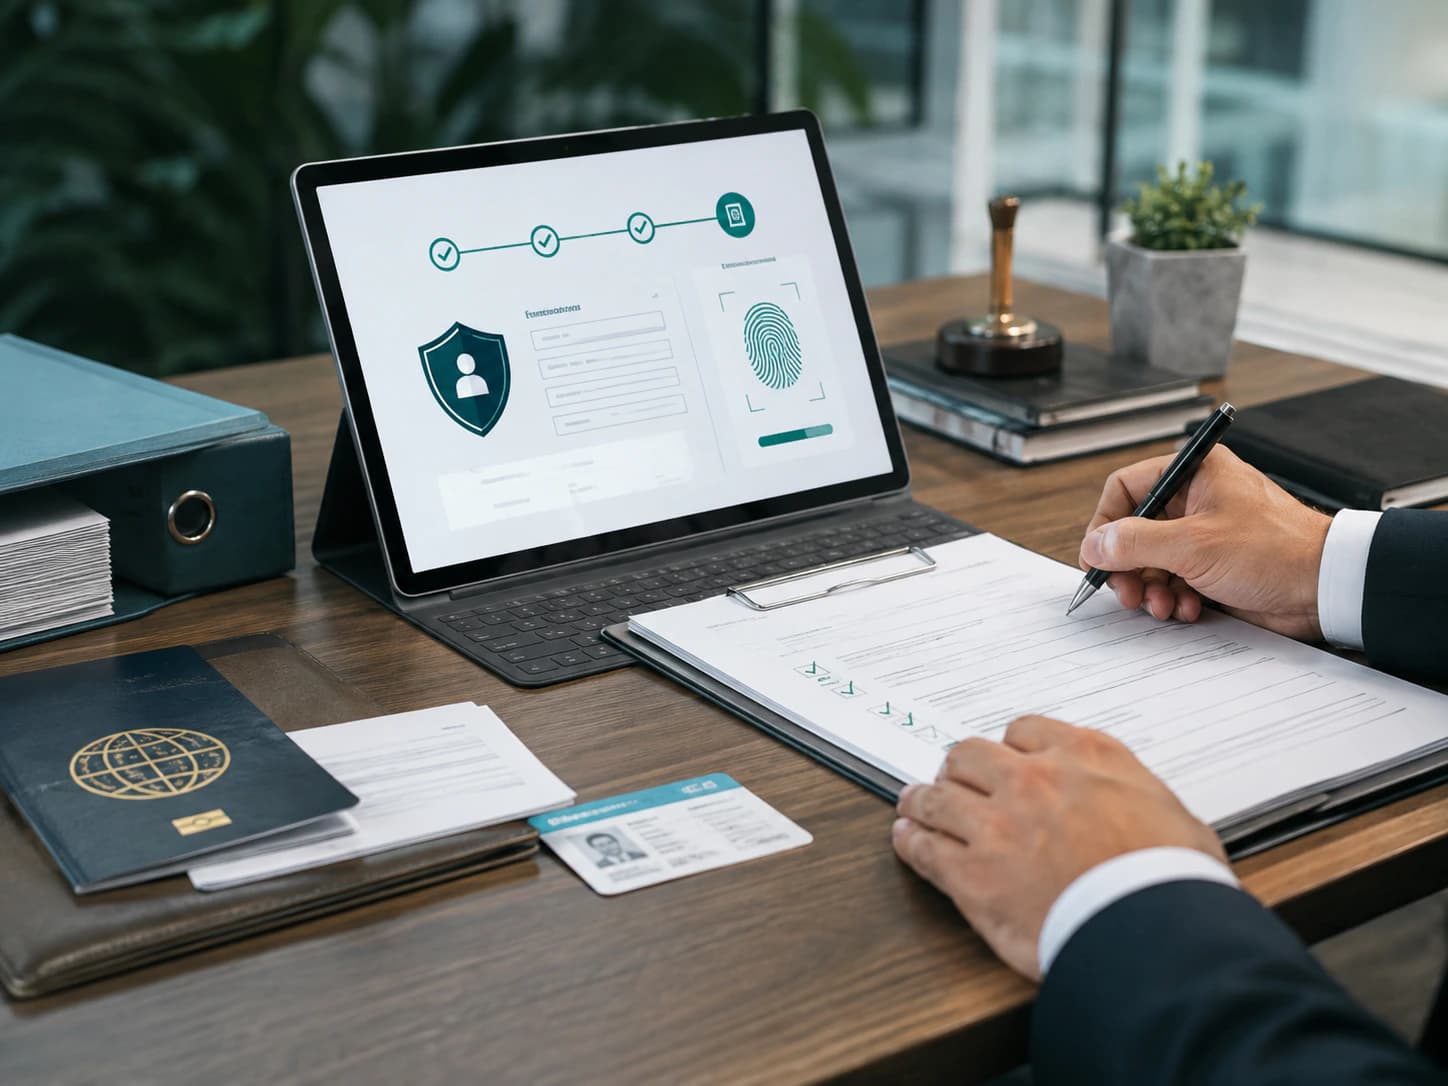
Retain structured evidence for consent, rights handling, incidents, and governance decisions.
Reduce repeated manual effort and expensive emergency remediation cycles.
Most delays come from operating-model gaps, not tooling gaps. Teams move faster when ownership, policy, architecture, and evidence align before implementation begins.
Teams pick dashboards and UI features without validating control coverage and integration depth.
Manual trackers break under request volume and cannot support reliable evidence retrieval.
Consent, rights requests, processor risk, and governance reporting sit in separate systems with no shared control plane.
Evidence is stitched from multiple systems under deadline pressure, causing errors and credibility risk.
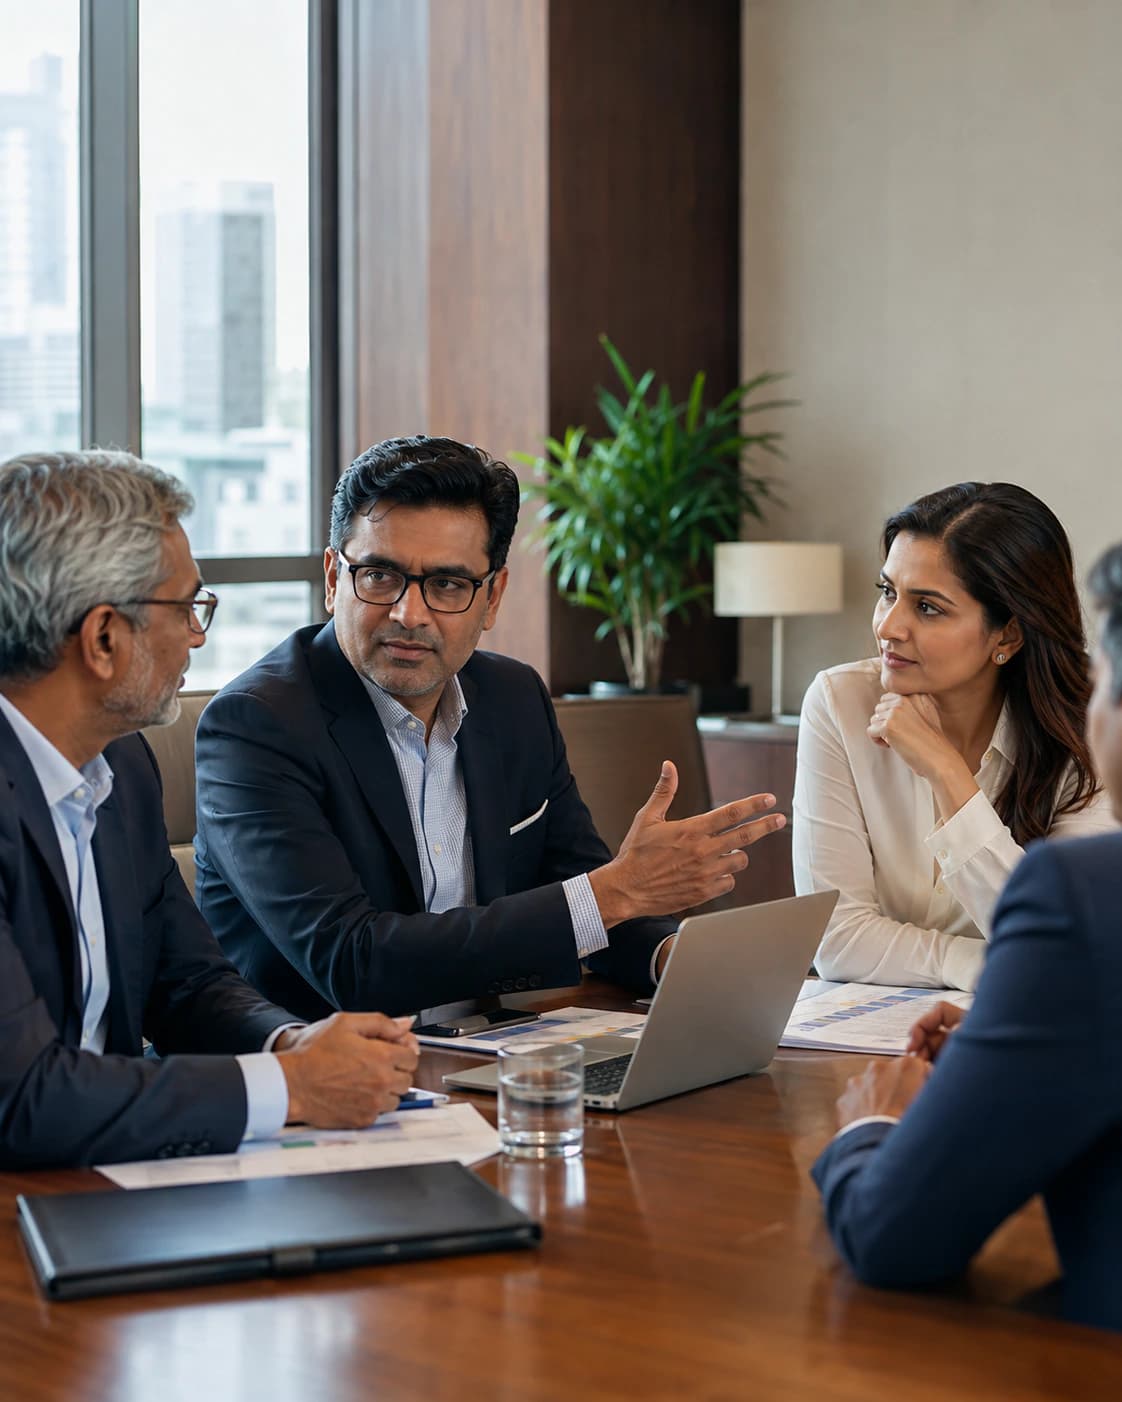
Made for the leaders who must turn DPDP obligations into connected controls, accountable workflows, and evidence their organization can retrieve on demand.
Choose this approach when privacy, technology, and operations leaders need one execution system—not another disconnected compliance tool.
Required controls prioritized against business risk and integration complexity.
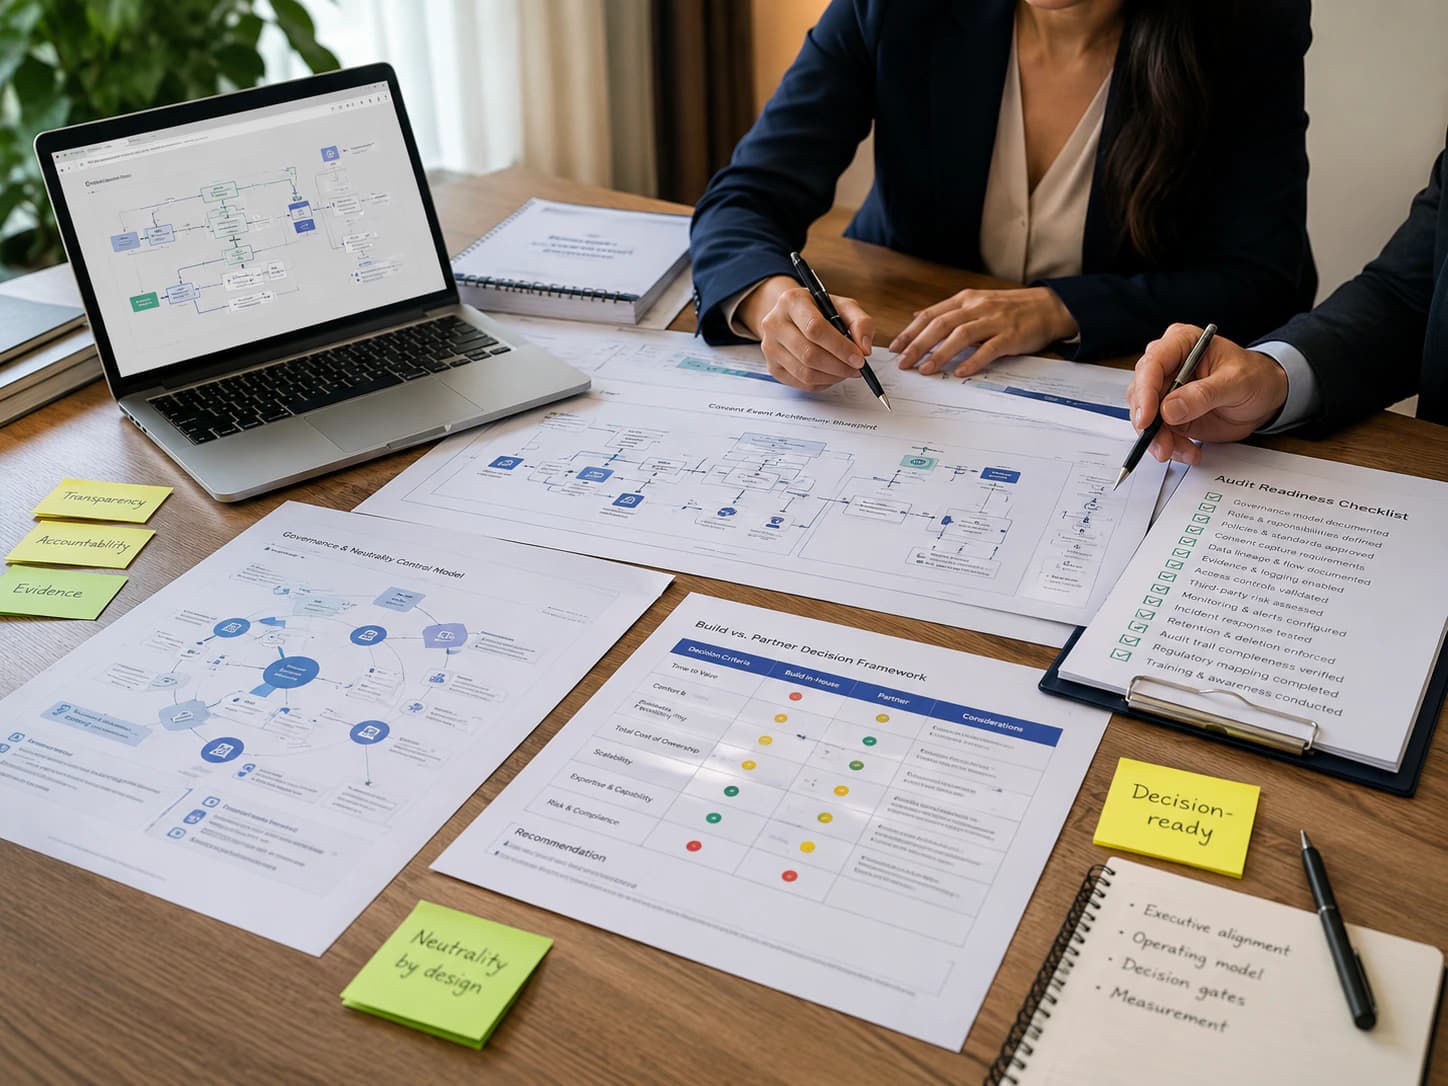
Prioritize software capabilities against your highest-risk obligations and workflows using a DPDP compliance checklist before finalizing implementation scope.
Connect customer data platforms, apps, support systems, and processor interfaces.
Enable owner accountability, escalation policies, and recurring control reviews.
Use periodic control testing, evidence snapshots, and data protection platform controls to maintain audit readiness.
Without a unified operating model
DPDP-specific workflows
Generic global templates with adaptation overhead
Engineering integration depth
UI-centric tools with weak backend orchestration
Audit evidence readiness
Manual evidence stitching under deadline pressure
AquaConsento operating model
DPDP-specific workflows
Purpose-built for Indian regulatory context
Engineering integration depth
API-first, integration-driven operations
Audit evidence readiness
Evidence lifecycle built into workflow design
DPDP compliance software helps enterprises operationalize India's Digital Personal Data Protection Act by managing consent records, Data Principal rights workflows, processor governance, audit evidence, and internal accountability in one system. It helps teams move beyond spreadsheets and manual trackers by connecting compliance controls with real operational workflows.
Use these linked pages together to cover strategy, controls, implementation, and evidence.
September 2026 · 6 min read
September 2026 · 6 min read