Strategic Clarity
Assess whether your organization should operate a DPDP Consent Manager for India or partner with one.
Use a governance-first framework to decide whether to build your own Consent Manager capability or integrate with one.
Consent Manager strategy is not a feature choice. It is an operating model decision covering neutrality, interoperability, accountability, and auditable lifecycle control.
Section 10
DPDP Act Consent Manager Provision
Anchor the operating model in the Act’s Consent Manager provision.
24/7
Consent Operations Uptime
Keep consent workflows available for continuous review and action.
MEITY
Registration Authority
Evaluate registration and accountability expectations before choosing a path.
Section 10 of the DPDP Act introduces the Consent Manager as part of India’s broader DPDP compliance framework. A DPDP Consent Manager for India helps individuals manage consent across multiple data fiduciaries through a single, transparent interface.
For most enterprises evaluating a Consent Manager in India, the question is not "should we become one?" but "should we build our own consent management capability or integrate with a registered Consent Manager?" Both paths have trade-offs in cost, control, compliance burden, and time-to-readiness.
 01 / 03
No. Many organizations should integrate with a Consent Manager instead of operating one directly.
Each outcome maps to execution, ownership, and proof — not abstract policy language.
Assess whether your organization should operate a DPDP Consent Manager for India or partner with one.
Define operating controls before committing engineering resources.
Avoid late-stage redesign by validating controls and evidence requirements upfront.
Most delays come from operating-model gaps, not tooling gaps. Teams move faster when ownership, policy, architecture, and evidence align before implementation begins.
Teams compare UI and feature lists instead of governance burden, liability posture, and operating complexity.
Engineering designs event flows before legal and governance controls are finalized, causing expensive rework.
Consent state exchanges and withdrawal propagation fail when interface contracts, identifiers, and consent lifecycle management controls are inconsistent.
Without clear neutrality, ownership, evidence models, and a reliable data protection platform, enterprise adoption and regulator confidence both suffer.
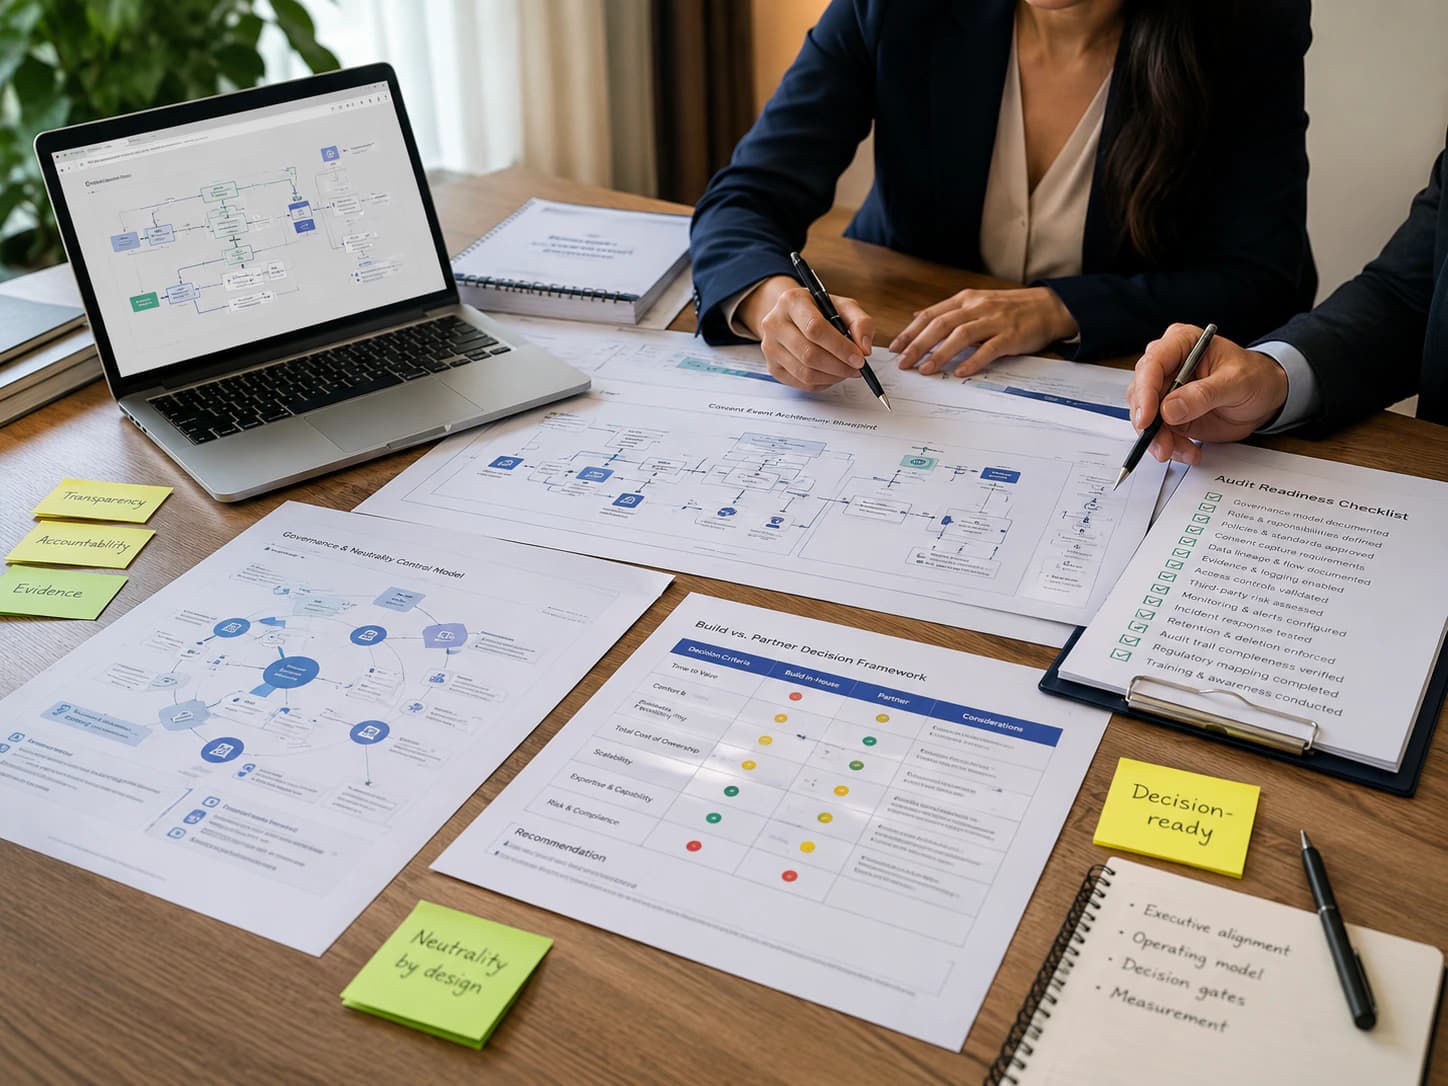
Make the Consent Manager decision with the right people in the room. This working session turns competing priorities across business, policy, product, and engineering into one clear direction before delivery teams begin designing against assumptions.
Built for the people who need to make a confident build, partner, and operating-model decision before commitments become expensive to reverse.
Move from decision framing to governance, integration, and validation through a phased delivery path that keeps ownership, evidence, and operating confidence clear at every step.
Align leaders on build-vs-integrate criteria, ownership boundaries, and decision gates. Establish business case, risk tolerance, and operating responsibilities before solution design.
Define whether consent infrastructure is a core strategic moat or better handled via integration.
Document neutrality, ownership, escalation, liability boundaries, and assurance expectations.
Specify lifecycle events, APIs, identity checks, interoperability contracts, and downstream enforcement through a scalable consent management platform.
Test evidence retrieval, incident playbooks, and operational readiness before scale.
Align leadership, governance, engineering, and operations around the value each team needs to deliver.
Without a unified operating model
Build-vs-integrate decision support
Feature-led selection with weak governance view
Control-to-evidence mapping
Documentation-heavy but low operational traceability
Execution model
Linear implementation that delays readiness
AquaConsento operating model
Build-vs-integrate decision support
Structured decision matrix with operating implications
Control-to-evidence mapping
Explicit links between controls and auditable artifacts
Execution model
Legal-tech-ops parallel execution guidance
No. Becoming a registered Consent Manager is not mandatory for every organization. Under DPDP, a Consent Manager is a registered intermediary that helps Data Principals give, manage, review, or withdraw consent. Most enterprises should first assess whether they need to build Consent Manager capability internally or integrate with a specialized Consent Manager while strengthening their own consent governance, evidence, and accountability controls.
Use these linked pages together to cover strategy, controls, implementation, and evidence.
September 2026 · 8 min read
September 2026 · 6 min read
September 2026 · 8 min read
September 2026 · 6 min read
September 2026 · 8 min read