A company can have a carefully reviewed privacy notice and still have a serious notice problem.
Imagine a financial-services business preparing for DPDP compliance. Legal has reviewed the website notice. Product has mapped the mobile-app onboarding flow. Compliance believes the main customer journeys are covered.
Then an operational review finds three things nobody had included: one branch is still using an older application form, support agents regularly receive identity documents through tickets, and a channel partner is sending prospect information directly into the CRM through an API.
None of those collection points is unusual. That is exactly why they are easy to overlook.
Before notice operations scale, the organisation needs to know where personal data actually enters the business, what is collected there, why it is collected, which notice applies, who owns the journey and where the information goes next.
A useful working map is:
Collection point → personal data → purpose → notice → owner → destination system
This is not a statutory register prescribed by the DPDP Act. It is a practical readiness control that can help Privacy, Legal, Product and Engineering find operational gaps before those gaps are repeated across dozens of systems and customer journeys.
Start with the legal position, not assumptions about compliance
For teams working on DPDP Act compliance, notice operations ultimately connect back to Section 5 of the Digital Personal Data Protection Act, 2023.
Section 5 provides that a request for consent is to be accompanied or preceded by a notice informing the Data Principal about the personal data and the purpose for which it is proposed to be processed, the manner in which applicable rights may be exercised, and the manner in which a complaint may be made to the Board.
The final Digital Personal Data Protection Rules, 2025 add further detail. Rule 3 says the notice should be understandable independently of other information and, in clear and plain language, include an itemised description of the personal data and the specified purpose or purposes of processing.
The timing matters.
As of 19 November 2026, Section 5 of the DPDP Act and Rule 3 of the final Rules are not yet operative. The Central Government's DPDP Act commencement notification places Sections 3 to 5 of the Act in the 18-month commencement tranche from 13 November 2025, while the final Rules place Rule 3 in the corresponding 18-month tranche. That points to 13 May 2027 for those provisions to come into force.
An organisation building a notice inventory today should therefore describe it accurately. It is a readiness and implementation control supporting DPDP compliance in India, not a statutory requirement to maintain a spreadsheet with these particular fields.
That distinction is important. Good compliance content should separate what the law requires from what practitioners recommend to make the law operational.
The collection point often tells you more than the system name
Return to the financial-services business.
Its CRM is already in the technology inventory. So are the mobile application, customer-support platform and workflow system. On paper, the major systems processing personal data are known.
But that does not tell Privacy how the information arrived there.
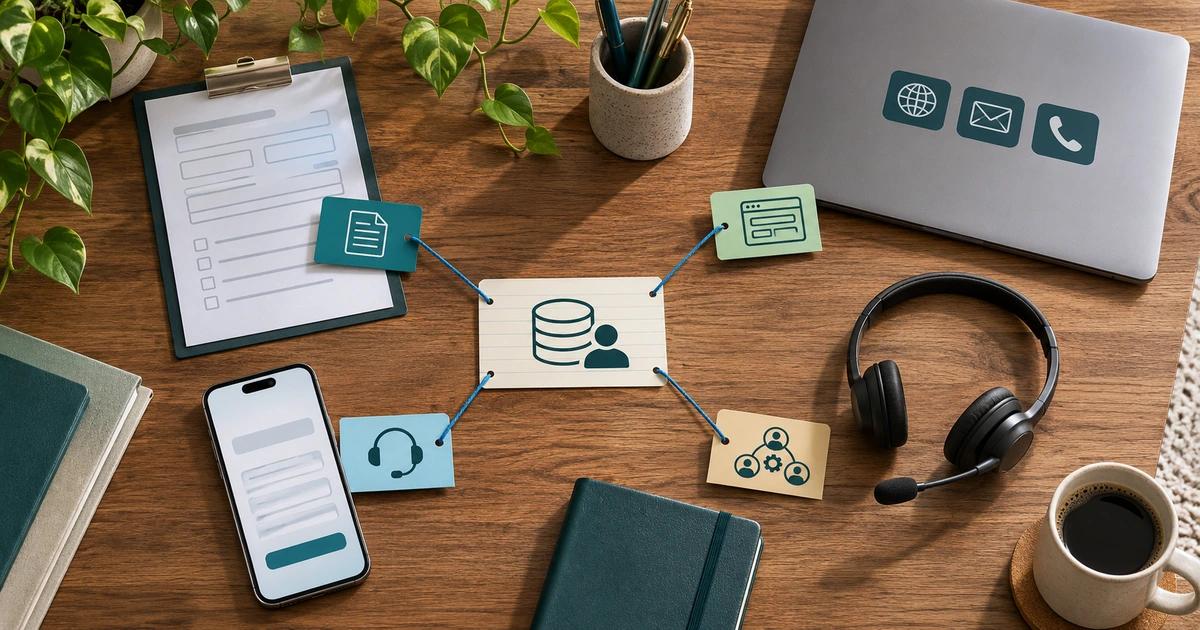
The CRM may receive data from a website enquiry, a branch application, a salesperson, a dealer, a partner API and a call centre. Those routes may involve different personal data, purposes, business owners and notice experiences even though they eventually lead to the same database.
For notice operations, the starting question should therefore be different.
Instead of asking only:
Which systems contain personal data?
ask:
Where does personal data first enter our organisation or become available to one of our systems?
That small change in perspective can expose collection points a conventional application inventory never shows.
Build the notice inventory around real customer journeys
A first inventory does not need sophisticated software. A spreadsheet is often enough to expose the problem, provided each row describes a real collection point rather than a broad department or technology platform.
For the business in our example, the first version might look like this:
| Collection point | Personal data | Purpose | Notice/version | Owner | Destination |
|---|---|---|---|---|---|
| Website enquiry form | Name, business email, phone, company | Respond to product enquiry | Web Notice v3 | Marketing | CRM |
| Mobile onboarding | Name, phone, account information | Create and administer account | App Notice v5 | Product | Customer platform |
| Branch application | Contact, application and supporting information | Process application | Branch Notice v2 | Operations | Workflow system |
| Support upload | Customer details and attachments | Investigate support request | Notice review required | Customer Support | Ticketing platform |
| Partner API | Prospect/customer information | Partner-originated customer workflow | Mapping to be confirmed | Partnerships | CRM/API layer |
The table is useful because incomplete rows become visible work.
“Notice mapping to be confirmed” tells Privacy where to investigate. “Owner unknown” reveals an accountability gap. A purpose that no longer matches the workflow gives Product and Legal something specific to resolve.
Compare that with a compliance tracker containing a row that simply says:
Privacy notice — in progress.
The second description says almost nothing about where the actual risk sits.
Walk the journey instead of reviewing only the documentation
One of the easiest ways to uncover forgotten collection points is to follow an actual customer journey from beginning to end.
Suppose a prospect first sees an advertisement and completes a landing-page form. A salesperson calls and records additional notes in the CRM. The prospect later visits a branch and supplies supporting information. Months later, as a customer, the same person uploads another document through the support portal.
Now follow the information through those steps.
The website form may already use an approved notice. The branch may still have an older form saved locally. The salesperson might collect an additional detail that never appeared in the original journey map. The support team may have enabled document uploads after the privacy review was completed.
A useful discovery technique is what I call the Edge Walk Test.
Rather than starting with central policies or systems, walk through the edges of the operating process: where Marketing hands a lead to Sales, where Sales hands a customer to Operations, where a partner sends information into an API, or where Support starts collecting information that was not part of the original product design.
These hand-offs are often where an otherwise organised DPDP compliance programme develops blind spots.
Purpose descriptions need to reflect what the business actually does
Once collection points are visible, purpose mapping becomes easier to test.
The difficulty is that many organisations use purpose labels that are too broad to be operationally useful.
Consider:
Marketing
versus:
Respond to the individual's request for information about the product
The second tells Legal, Product and Marketing much more about the processing activity being described.
The same problem appears with phrases such as:
- business use;
- customer management;
- service delivery;
- analytics.
Those labels may group activities internally, but they are often too broad to help teams understand whether the notice, product flow and downstream system are describing the same activity.
In Digital Personal Data Protection Rules, 2025, Rule 3's final wording refers to the specified purpose or purposes of processing and a specific description of the goods, services or uses enabled by that processing.
For implementation, that means the inventory should help teams compare three things:
What does the notice say?
What does the business owner say the data is used for?
What do the connected systems actually do with it?
If the website collects data to respond to an enquiry but the CRM automatically places that person into a separate promotional workflow, the inventory has surfaced something worth reviewing.
That is a practical bridge between DPDP Act compliance and day-to-day system behaviour.
Offline processes can disappear from a digital compliance programme
Digital channels usually receive the most attention because they are easy to see and test.
Offline and assisted processes are messier.
Take the branch from our example. During a network outage, staff use a printed application form. Later, they scan the completed document and upload it into the central workflow system.
The destination system may already appear in the data inventory, but the actual collection happened earlier—at the branch counter.
That means the organisation needs to understand which notice or information was available at that point, who owns the form, how the form is version-controlled and how changes approved centrally eventually reach the branch.
Call centres create similar problems.
A central script might be updated, but a regional team may still be using an older locally saved version. Agents may also ask for additional information because it helps resolve a case, even though that information was never included in the documented process.
These are not exotic privacy scenarios. They are ordinary operational behaviours.
That is why DPDP compliance in India cannot be approached only through websites, apps and policy documents. The discovery work needs to include the real channels through which people interact with the business.
APIs and partners need a different kind of notice mapping
Partner-originated data can be harder to map because the enterprise receiving the information may never have displayed a collection screen to the individual.
Suppose a dealer collects:
- name;
- phone number;
- location;
- product interest.
The dealer then sends those fields directly into the enterprise through an API.
Technically, the enterprise API is the point where the data enters its environment.
Operationally, however, the interaction with the individual happened somewhere else.
A useful notice inventory should preserve both facts.
It should help Privacy understand where the information originated, which party interacted with the individual, what purpose is associated with the flow, which internal system receives the data, and who owns the partner relationship.
The inventory should not try to determine the legal answer automatically. Different commercial relationships may require different analysis.
Its job is to make the flow visible enough for Legal or Privacy to reach the right conclusion.
Ownership is what stops the inventory becoming obsolete
Creating the first inventory is usually easier than keeping it accurate.
The business keeps moving.
Marketing adds a new field to a landing page. Product changes onboarding. Customer Support enables another attachment type. A branch updates its form. Engineering publishes a new API endpoint. A new partner begins sending an additional data field.
If Privacy owns every change, the inventory eventually falls behind.
A better operating model gives the team closest to the collection point responsibility for identifying relevant changes, while Privacy or Legal maintains the review standard.
Marketing does not need to make the final legal decision every time a form changes. It does need to recognise that adding a new personal-data field may trigger a review of the purpose and notice mapping.
The same logic applies to Product, Support, Operations, Engineering and Partnerships.
A practical trigger is:
Review the collection-point record whenever the personal data, purpose, notice, owner, source, partner or destination materially changes.
This makes the inventory part of change management instead of another annual privacy exercise.
Use a five-field check to find the weakest rows
Once the first inventory exists, choose any collection point and see whether the organisation can answer five things without assembling several teams for a meeting.
Can it identify:
- where personal data enters;
- what personal data is collected;
- why it is collected;
- which notice or notice version applies; and
- Who owns the collection point and destination system?
An unclear answer does not automatically mean the organisation is violating the DPDP Act.
It means the row needs investigation.
Perhaps the issue is simply unclear ownership. Perhaps an old notice is still being used. The purpose may be too broad, or the destination system may have changed without the privacy documentation being updated.
The value of the inventory is that it converts a vague concern into a specific operational task.
“DPDP compliance needs improvement” is difficult to assign.
“The partner API has no mapped notice source” can be assigned tomorrow.
Technology becomes useful once the operating model is understood
A spreadsheet may be sufficient during initial discovery. It becomes harder to manage when hundreds of collection points need to stay connected with purposes, notice versions, owners, systems, consent states, rights workflows and evidence.
This is where software can support the process, but the order matters.
The organisation first has to understand what it is trying to govern.
For teams building operational controls for DPDP compliance, the useful role of a compliance platform is to help connect approved requirements with the operational workflows where personal data is collected and acted on.
The platform cannot decide which undocumented collection points exist inside the organisation. It cannot replace Legal's determination of the appropriate notice or purpose.
What it can do is support a more structured operating model once those decisions have been made.
That distinction also helps avoid one of the common problems with compliance technology: implementing software before the organisation has agreed what the software needs to govern.
The inventory needs to survive the next product release
The first notice inventory is a baseline. Its real value appears after several months of product releases, campaign changes, partner integrations and operational workarounds.
If Product adds another field, the corresponding row should be reviewed.
If Marketing launches a new lead form, the collection point should be added rather than discovered six months later.
If a branch process is retired, the old row should be marked inactive rather than disappearing without explanation.
If a partner starts supplying additional customer information, the organisation should understand the new source, purpose and ownership before that data simply becomes another field in the CRM.
This is what turns the inventory into a sustainable DPDP compliance control.
The organisation moves beyond asking: Do we have a privacy notice?
It can ask: Do we know every important place personal data enters, why we collect it, which notice applies, who owns that journey and where the information goes next?
For organisations preparing for DPDP compliance in India, answering that question before May 2027 is more useful than producing another policy document that may never reach the forgotten collection points where personal data is actually entering the business.
Frequently Asked Questions
Is a DPDP notice inventory legally required?
No specific register called a “DPDP notice inventory” is prescribed by the DPDP Act or final Rules. The inventory described here is a recommended implementation and readiness control designed to help organisations map collection points, personal data, purposes, notices, owners and systems.
When do the main DPDP notice requirements come into force?
Section 5 of the DPDP Act is in the 18-month commencement tranche under the DPDP Act commencement notification, as is Rule 3 under the final Rules. Based on the published commencement notification and final Rules, those provisions are scheduled to come into force on 13 May 2027.
Should offline forms and call-centre processes be part of the inventory?
Yes, where they form part of personal-data collection journeys. Limiting discovery to websites and mobile apps can miss branch forms, call-centre workflows, paper-assisted processes, support uploads and other operational channels.
Should partner APIs be included in DPDP notice mapping?
Where a partner or API forms part of the personal-data collection journey, the organisation should understand the data source, purpose, applicable notice path, operational owner and destination system. The appropriate legal treatment should then be assessed based on the specific relationship rather than inferred from the technology alone.
How often should the notice inventory be reviewed?
The Act does not prescribe a universal review interval for the operational inventory described here. A sensible approach is to trigger review when the data collected, purpose, notice, collection channel, partner, owner or destination system changes, supported by periodic governance reviews appropriate to the organisation.
A notice inventory cannot make an organisation compliant by itself, and it should never be presented as though maintaining this particular artefact guarantees DPDP Act compliance.
Its value is operational.
It gives Privacy, Legal, Product, Engineering, Marketing and Operations a shared picture of how personal data actually enters the organisation. That makes gaps easier to identify, ownership easier to assign and approved notice requirements easier to connect with real customer journeys.
Before notice operations scale, find the collection points first. Otherwise, an organisation can spend considerable effort perfecting the right legal wording while an old form, partner API or support workflow continues collecting data somewhere nobody remembers to review.