A DPDP software demo can look impressive very quickly. There is a dashboard, a consent module, request tracking, processor records, audit logs and perhaps a compliance score showing how much work has been completed.
The more revealing question comes after the demo:
How does the software know that all of those records belong to the same privacy story?
Consider one customer. Kavya gives consent for promotional communication while Notice Version 2 is active. Months later, the organisation publishes Version 3. Kavya then withdraws marketing consent and, during the same period, asks the company to correct an inaccurate profile field. One of the relevant systems is operated by an external processor.
Good DPDP compliance software should be able to connect those events without forcing Privacy, Legal and Engineering to reconstruct the story from separate tickets, screenshots and application logs.
That is fundamentally a data-model question.
The real test is what sits underneath the dashboard
Many organisations already have systems that can store individual pieces of a privacy programme.
CRM has the customer record. The application database records a consent flag. Legal keeps notice versions in a document repository. Support creates tickets for customer requests. Procurement maintains processor information, while Engineering has logs showing whether downstream changes actually happened.
Nothing appears to be missing.
Then somebody asks a simple question about Kavya:
Which notice did she see when she gave consent, which purpose did that consent cover, when did she withdraw it, what systems acted on the withdrawal, and what evidence shows that the process finished?
Suddenly, five technically complete systems become one incomplete answer.
This is why a useful privacy platform needs more than storage. It needs relationships between the records.
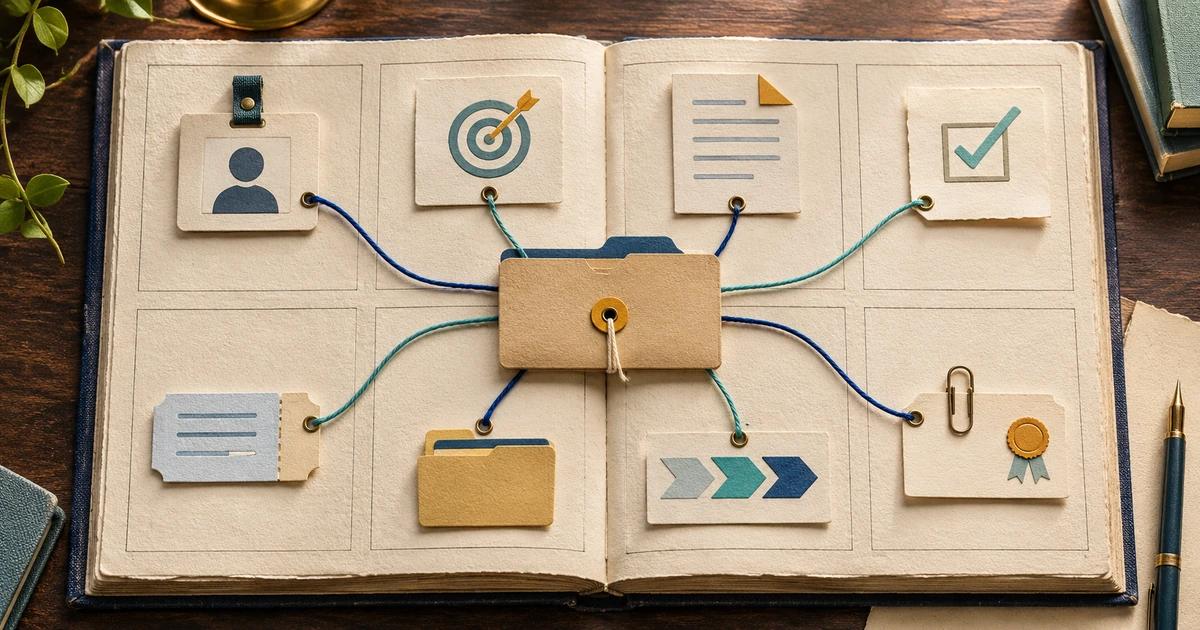
A practical model can be built around eight core objects: Data Principal, purpose, notice, consent, request, processor, workflow and evidence.
The DPDP Act does not prescribe these eight software objects. They are an implementation model for testing whether the system can preserve the context behind real privacy operations.
Start with the person and the purpose, not the ticket
Kavya's privacy history needs somewhere stable to begin.
The first object is the Data Principal: the individual to whom the relevant personal data relates. The Digital Personal Data Protection Act, 2023 uses this term throughout the statutory framework.
In software, that does not mean building another full CRM. It means maintaining enough reliable identity context to connect Kavya's relevant consent states, requests and events even if her email address or mobile number later changes.
The second object is the purpose.
This is where many generic systems become too simplistic. A record saying consent = yes tells the organisation very little unless it also knows what Kavya said yes to.
Promotional communication may be one purpose. Optional analytics may be another. Personalised offers may require a different decision again.
The Act connects consent to a specified purpose. From an architectural perspective, that means the purpose should not exist only as text buried inside a notice PDF. It needs to be something the system can reliably associate with consent, workflows and later changes.
For Kavya, the meaningful relationship is therefore not:
Kavya → Consent = Yes
It is closer to:
Kavya → Promotional Communication → Consent Granted
That extra context becomes important as soon as another purpose enters the picture.
The notice explains what the person was told at the time
Now add the third object: the notice.
Suppose Kavya gave consent while Notice Version 2 was displayed. Six months later, Legal approves Version 3.
Publishing the new notice should not silently rewrite Kavya's earlier record so that it appears she saw Version 3 when she did not.
A trustworthy system preserves the version that was actually associated with the event.
The final Digital Personal Data Protection Rules, 2025 provide operational detail for notices under Rule 3, including requirements relating to the personal data and specified purposes described in the notice once that rule becomes operative. Rule 3 is scheduled for the eighteen-month commencement stage after publication of the Rules on 13 November 2025.
The architectural lesson is useful even before that commencement date: historical events should remain connected to their historical context.
If a new notice version replaces an older one, the software should be able to show both the current notice and the version associated with Kavya's original decision.
Consent needs history, not just a current value
The fourth object is the consent record itself.
A practical consent event should preserve enough context to answer what happened without asking several teams to interpret the database.
For example:
Kavya + Promotional Communication + Notice v2 + Granted + 14 January + Mobile App
Later:
Kavya + Promotional Communication + Withdrawal + 21 August + Preference Centre
The latest state may now be “withdrawn,” but the January event should not disappear.
This is where data privacy compliance software differs from a simple preference table. The latest value is operationally useful, but the history explains why that value exists.
If the platform keeps only the current flag, it may be able to stop a campaign today while being unable to explain what happened six months ago.
A request should connect to the privacy outcome, not end at “ticket closed”
Kavya also submits a correction request because her profile contains an outdated address.
A generic ticketing system can record:
Ticket #4582 — Closed
That tells a manager that somebody completed a task.
It does not necessarily show what happened to Kavya's personal data.
The request object needs enough privacy context to show who made the request, what type of request it was, what information or systems were involved, which workflow followed, and what outcome was reached.
This distinction matters because privacy operations cross systems.
Support may receive the request. Privacy may assess it. Engineering may update one system. Another application may require separate action. An exception may need Legal review.
The useful record is not simply that the ticket disappeared from an open queue. It is that the relevant privacy outcome can be traced.
Processor records become useful only when they connect to real processing
The sixth object is the processor.
The DPDP Act defines a Data Processor as a person who processes personal data on behalf of a Data Fiduciary.
Many organisations already maintain vendor or processor registers. The architectural question is whether that information actually connects to privacy operations.
Suppose an external provider handles part of Kavya's promotional communication workflow. When Kavya withdraws consent, does the software know that this processor is part of the affected processing chain?
A static processor profile may contain the company name, contract date and security documentation. Useful information—but none of it proves that Kavya's withdrawal reached the relevant downstream process.
A stronger model can connect processors to the purposes and workflows in which they participate.
That relationship makes the register operational rather than purely documentary.
Workflow is where the records turn into action
The seventh object, workflow, is not a statutory DPDP object. It is an implementation mechanism.
It is also where the data model becomes practical.
Kavya's withdrawal may need to update a consent store, CRM eligibility and a campaign system. Her correction request may involve Support and Engineering. A processing exception may need to move to Legal before the case can close.
The workflow should preserve how that action moved through the organisation:
trigger → owner → action → exception → outcome
The reason to model this explicitly is not to automate every privacy decision.
Some actions can be automated safely when the inputs and rules are clear. Others require judgement.
A workflow can recognise that a case requires Legal review and route it appropriately. It should not invent the legal conclusion merely because a rule engine wants a final status.
For buyers evaluating DPDP compliance software in India, this is an important distinction. “Automation” means much more when the platform is operating on well-defined privacy records than when it simply moves generic tickets between queues.
Evidence should explain what the workflow actually did
The eighth object is evidence.
This does not mean creating a digital warehouse containing every screenshot, email and system log.
The better question is: what would someone need later to understand what happened in Kavya's case?
For the original consent, that may include the purpose, notice version, choice, timestamp and channel.
For the withdrawal, evidence may include the event itself, downstream system acknowledgement, an exception where one existed, and the eventual resolution.
For the correction request, the useful trail could show receipt, ownership, system action and closure.
Evidence is much easier to use when it remains attached to the event it supports.
AquaConsento's separate analysis of reconstructing DPDP compliance evidence from operational events goes deeper into what enterprises may need to prove. The architecture point here is simpler: dumping evidence into a common folder after a workflow closes is not the same as preserving the relationship between evidence and the event it proves.
The eight objects should behave like one connected privacy story
The individual object names matter less than the connections between them.
Kavya's case might look conceptually like this:
| Privacy record | What the system should be able to show |
|---|---|
| Data Principal | Kavya's privacy identity |
| Purpose | Promotional communication |
| Notice | Version 2 associated with the original consent |
| Consent | Granted in January, withdrawn in August |
| Request | Correction request for inaccurate profile data |
| Processor | Relevant third party involved in an applicable workflow |
| Workflow | Actions triggered by withdrawal and correction |
| Evidence | Events, acknowledgements, exceptions and closure records |
This is not intended as a literal database schema.
The test is whether the software understands enough of these relationships that a user can reconstruct the privacy story without manually joining data from separate modules.
That is the difference between eight features and one operating model.
Audit logs are useful, but they are not the data model
Nearly every enterprise platform has logs.
That does not automatically make it a privacy system of record.
An audit log might say: User 843 changed field X at 14:32.
A support ticket may separately say: Marketing withdrawal completed.
Compliance still needs to know whether both records concern Kavya, the same purpose and the same underlying event.
Without those relationships, the organisation has evidence fragments rather than an evidence chain.
This is why buyers should be careful when a DPDP compliance tool is described as “audit ready” simply because it records user activity.
Ask what each log entry is connected to.
Can it be traced back to a specific consent event, purpose, request, processor action or workflow outcome?
If the answer depends on somebody interpreting free-text comments, the architecture may still be fragmented.
The best buying test starts with one customer, not the feature menu
A vendor demo normally follows the product navigation.
Consent module first. Rights module next. Processor section after that. Audit logs at the end.
Reverse the test.
Give the vendor one realistic customer case and ask them to follow it through the platform.
Start with Kavya's original consent. Ask which notice she saw and which purpose it covered. Then publish a new notice version without changing her historical event.
Next, withdraw her marketing consent.
Create a downstream failure so one system does not acknowledge the change immediately.
Submit a correction request.
Add a processor dependency.
Then ask the vendor to show what evidence remains when everything is eventually resolved.
The most useful question is not: “Do you have all eight features?”
It is: “Can you reconstruct the customer's privacy history without leaving the operating model?”
This is the One-Customer Reconstruction Test.
It reveals architecture far more effectively than a polished dashboard.
If the vendor has to open several disconnected modules, compare timestamps manually and interpret ticket comments to explain what happened, the platform may still be fragmented even though everything appears under one login.
A good data model also makes automation safer
The benefit of structured privacy records is not limited to audits.
Automation becomes more reliable when the software knows what it is acting on.
If a withdrawal is explicitly connected to Kavya and to the promotional-communication purpose, the workflow can target the appropriate downstream actions.
If a processor participates in that purpose, the platform can surface the dependency.
If an exception occurs, the workflow can preserve it as unresolved rather than marking the entire case complete simply because one task finished.
The architecture creates boundaries around automation.
That is considerably safer than automating generic ticket text or loosely structured status fields.
The Act defines obligations and entities, not your database tables
This distinction should remain explicit.
The DPDP Act defines legal concepts such as the Data Principal, Data Fiduciary, Data Processor and specified purpose. It also establishes the statutory framework around consent, notices and Data Principal rights.
The final DPDP Rules add operational detail and apply on a phased commencement timetable. Rules 3 and 5–16, among others, are scheduled to commence eighteen months after publication on 13 November 2025.
Neither source says a compliance platform must use an eight-object data model.
That model is an architectural recommendation.
Its purpose is to help buyers distinguish between software that merely stores compliance activity and software that preserves the relationships needed to operate and explain that activity.
Those are not the same thing.
What should DPDP compliance software ultimately give you?
The answer is not “more records.”
It is connected to records.
AquaConsento's current DPDP software positioning describes an operating layer connecting user consent management, rights requests, processor governance and audit evidence rather than leaving them in separate systems.
For teams evaluating software that connects privacy records, workflows and evidence, the important question is whether those capabilities really share context underneath the interface.
A consent should know its purpose and notice history. A request should know which Data Principal it belongs to. A workflow should know what triggered it. Processor involvement should remain visible where it matters. Evidence should point back to the event it proves.
When those relationships survive, the software becomes more than a collection of privacy modules.
It becomes an operating model that people can actually interrogate.
The useful system is the one that can still tell the story later
Months after Kavya gave consent, nobody should have to remember which screen she used or which spreadsheet Legal maintained at the time.
The record should explain itself.
It should show that she saw a particular notice, agreed to a particular purpose, later withdrew that permission, submitted a correction request, triggered operational work and left behind enough evidence to understand the outcome.
That is the real value of the eight-object model.
Not eight boxes.
Not eight database tables.
A connected privacy history that still makes sense after the workflow has moved on.
For DPDP compliance software, that is a much more meaningful buying standard than the number of widgets on the dashboard.
Frequently Asked Questions
What should DPDP compliance software store?
A practical system should be able to connect records concerning the Data Principal, purpose, notice or notice version, consent history, privacy requests, relevant processor relationships, operational workflows and evidence. The exact schema can vary by organisation and product.
Is a ticketing tool enough for DPDP compliance?
A ticketing system can be useful for assigning and tracking work, but tickets alone may not preserve relationships between purpose-level consent, notices, processor dependencies, privacy requests and operational evidence. The key question is whether the organisation can reliably reconstruct the underlying privacy outcome.
What should a useful consent record contain?
A consent record should generally preserve enough context to identify the relevant person, purpose, notice or consent context, choice, time, channel and later lifecycle changes. The exact design should reflect the organisation's processing model and applicable requirements.
Does the DPDP Act prescribe a software data model?
No. The Act and Rules define legal concepts and obligations but do not prescribe the eight-object architecture described here. This model is an implementation framework for evaluating whether privacy records remain connected and reviewable.
What should buyers test during a DPDP software demo?
Instead of checking modules individually, give the vendor one realistic customer journey involving consent, a notice change, withdrawal, a rights request, a processor dependency and an exception. Then test whether the platform can reconstruct the entire history and supporting evidence without manual data stitching.