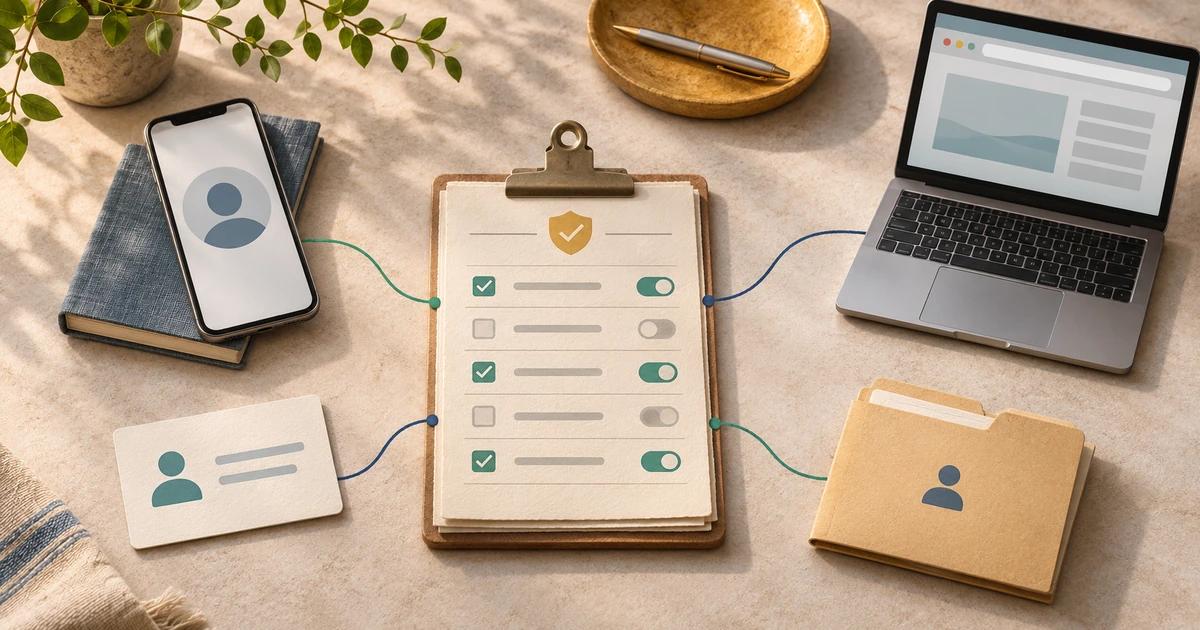
Meera looks like one customer to herself. Inside the company, she may look like four.
CRM recognises her email address. The mobile app uses a customer account ID. An SMS platform works from her phone number. Before she logged in, the website knew her through a browser or device identifier.
Then Meera changes her marketing preference.
At that moment, the business has to answer a question that sounds technical but has a very practical consequence: which of those identities should receive the updated consent state?
Good user consent management should not simply update every record that looks similar. The organisation first needs reasonable confidence that the identifiers belong to the same person, and then it needs to know whether the consent relates to the same purpose.
Getting that wrong can create something more serious than a duplicate customer record. It can attach the right permission to the wrong person.
One customer can easily become several records
This happens naturally as customers move between channels.
Meera may first visit a website without signing in. The site creates an anonymous browser identifier. A week later, she registers with an email address. During onboarding she verifies a mobile number, and the customer platform creates an internal account ID.
From Meera’s perspective, nothing unusual has happened. She has simply moved from browsing to becoming a customer.
Inside the organisation, however, several systems may now know her differently.
The CRM may use the email address as its main reference. Marketing automation may rely on the mobile number. The app may use the internal customer ID. Analytics may still contain activity associated with the earlier anonymous browser identifier.
Identity resolution tries to work out whether those records belong to the same person.
Consent management has to answer a second question: if they do belong to the same person, which consent decisions should travel across those links?
Those questions are related, but they are not identical.
Matching the customer does not mean merging every consent
Suppose the CRM contains this record for Meera:
Promotional email: Yes
Her mobile-app profile contains:
Personalised offers: No
There may be no doubt that both records belong to Meera. That still does not make those two consent states interchangeable.
They relate to different purposes.
If the system merges both profiles into a single field called consent = yes, it has simplified the customer profile by destroying an important part of the customer’s choice.
This is why identity resolution has to work alongside consent lifecycle management, rather than replacing it.
The Digital Personal Data Protection Act, 2023 connects consent to a specified purpose and describes consent as free, specific, informed, unconditional and unambiguous, expressed through clear affirmative action.
The Act does not tell companies which customer-ID architecture to build. It does, however, reinforce a useful design principle: proving that two records belong to the same person is not enough to tell you that two permissions mean the same thing.
Email, phone, account and device IDs are not equally reliable
The temptation in a fragmented system is to choose one identifier and call it the customer.
That can work until the identifier changes.
An authenticated account ID is often a strong reference inside a company's own environment. A verified email or mobile number can also be a useful matching signal. But emails change. Phone numbers can be reassigned. Families sometimes share contact details. Devices can be used by several people.
A browser or device ID presents an even more obvious problem. It can tell the organisation a great deal about a technical session without necessarily proving who was behind the screen.
For consent purposes, the relevant question is therefore not simply:
Do these records share an identifier?
A stronger question is:
What evidence do we have that these identifiers currently belong to the same person?
That difference matters when the system is about to propagate a withdrawal, preference change or new permission across several customer systems.
A practical architecture can treat identifiers according to the confidence they provide rather than pretending they are all equivalent.
| Identifier | What it may help establish | What can go wrong |
|---|---|---|
| Authenticated customer ID | A strong internal link to an established account | Account structures can change, merge or include multiple users |
| Verified email | A strong contact and profile signal | Addresses can change, be shared or eventually reused |
| Verified mobile number | Useful identity and communication context | Numbers may be reassigned or shared |
| Device/browser ID | A device, browser or session context | One device may be used by several people |
| Anonymous identifier | Pre-login activity | It should not automatically become a known-person consent record |
This is not a hierarchy prescribed by the DPDP Act. It is an implementation discipline designed to prevent weak identity signals from making strong consent decisions.
Follow the person, purpose and history together
The cleanest way to think about this is not “Which identifier owns the consent?”
The consent should not really belong to the email address, phone number or device.
It should remain understandable in relation to the person, purpose and event history.
Take Meera again.
Her verified email and mobile number are linked to customer account CUS-28419. She later signs into the app from the same browser she used before registration. At that point, the business may have enough reliable information to connect several previously separate identifiers.
That can improve the customer view.
But it should not erase how Meera’s earlier decisions happened.
Suppose she accepted analytics while browsing anonymously, declined personalised offers after creating an account, and later withdrew promotional email through the app.
After identity resolution, the company may confidently understand that those activities all relate to Meera.
The consent history should still show three distinct decisions, three contexts and the purposes attached to each one.
A unified customer profile is useful.
A flattened permission history is not.
Shared devices expose weak matching logic very quickly
Consider a household tablet.
Ravi logs into an ecommerce account and opts into promotional communication. Later he logs out.
Priya then uses the same tablet.
If the consent system assumes that the device identifier still means “Ravi,” Priya’s activity can begin inheriting a consent state that was never hers.
Nothing necessarily looks broken. The database may actually look impressively consistent because every system is using the same state.
The problem is that the match itself is wrong.
Shared devices, recycled phone numbers, family email accounts and incorrectly linked CRM profiles all create versions of the same risk.
This is why a false merge can be more dangerous than an obvious duplicate. A duplicate usually announces itself: two profiles exist for one customer. A false merge can quietly apply one customer’s permissions to another person while appearing technically tidy.
When confidence is weak, link before you merge
Enterprise identity systems often want a binary answer: these records are either the same person or they are not.
Real customer data is rarely so cooperative.
Imagine two profiles share a mobile number but have different verified emails and different account IDs.
That could be a duplicate customer.
It could also be a shared family number.
Automatically merging the profiles would turn an uncertain identity signal into a definite consent decision.
A safer operating approach is to link before you merge.
The organisation can recognise that two profiles may be related while keeping their consent histories separate until stronger evidence appears. An authenticated login, verified profile update or another trusted internal event may later provide the confidence needed to merge them.
This is not a DPDP requirement. It is a governance pattern.
Its value is that the system does not need to pretend it knows more than it actually does.
A changed phone number should not create a new consent history
Six months later, Meera replaces her mobile number.
CRM is updated immediately. The app is already tied to her authenticated customer account. A marketing platform, however, keeps the old number for another week.
If consent was modelled as belonging to the number itself, the company now has a difficult question: does Meera’s previous permission belong to the old number, the new number or both?
A better architecture treats the mobile number as one identifier associated with Meera, not as Meera herself.
Once the change has been reliably authenticated, the current identity relationship can move to the new number while the historical consent record remains untouched.
The old event can still show that Meera made a particular choice at a particular time when the previous number was associated with her account. The current customer profile can separately show that the number is no longer active.
That distinction between current identity and historical provenance is what keeps the lifecycle understandable.
Account merges are where consent history can disappear
Profile duplication is common enough that customer-service teams eventually have to merge records.
Perhaps Meera registered once with her work email and later created another account using a personal address. Support confirms that both profiles belong to her and decides to consolidate them.
From a CRM perspective, that may look like straightforward housekeeping.
The consent history may tell a different story.
One profile contains a promotional opt-in from March. The second contains a withdrawal recorded in August.
If both events concern the same purpose, the later withdrawal may be highly relevant to the current state. But if the records concern different purposes, blindly applying “latest timestamp wins” can create the wrong result.
The merge therefore needs enough context to preserve what actually happened: the purpose, source identity, event time and relationship between the events.
AquaConsento’s existing article on recognising one consent event across retries and integrations addresses a related but different technical problem. It explains why one user action should not become multiple consent events merely because distributed systems retry the same message.
The distinction is useful:
Identity matching asks whether two records describe the same person. Event matching asks whether two records describe the same action.
A dependable consent system needs to handle both without confusing them.
Anonymous browsing becomes tricky after login
The anonymous-to-known transition is another place where systems can make overly confident assumptions.
Meera browses a site from her laptop before she has an account. The website creates an anonymous identifier.
Later she registers and logs in from the same browser.
It may be entirely reasonable for the organisation to connect some of that earlier activity with her known customer profile once a reliable authenticated event establishes the relationship.
The problem appears after she logs out.
If somebody else uses that laptop next, the browser identifier should not automatically behave as though Meera is still the person behind the screen.
This is the practical reason device identity needs to be treated as context rather than as a permanent substitute for human identity.
The DPDP Rules recognise that one person can appear through several digital presences
India's regulatory terminology also reflects this multi-identity reality.
Rule 2 of the Digital Personal Data Protection Rules, 2025 defines a “user account” broadly enough to include an online account and profiles, pages, handles, email addresses, mobile numbers and similar presences through which a Data Principal accesses a Data Fiduciary's services.
That definition does not prescribe an identity-resolution algorithm, nor does it tell enterprises to merge every email, phone number and profile into one customer record.
What it does show is that a single person can interact with an organisation through several digital presences.
For a consent management system in India, the architectural challenge is therefore to keep those identities connected enough for customer choices to remain reliable without turning every shared identifier into proof that two records are the same person.
As of November 2026, the DPDP framework itself also remains subject to phased commencement, so architectural recommendations such as identity confidence scoring or link-before-merge should not be presented as statutory requirements.
Test the awkward cases, not just the clean customer journey
Most implementation demonstrations are easy.
One customer has one email, one phone number and one account.
Production data is rarely that polite.
A more useful test includes customers who:
- replace their mobile number;
- change email addresses;
- create duplicate accounts;
- browse anonymously before registration;
- use multiple devices;
- share a device with another person;
- merge profiles after years of activity.
The important outcome is not whether the identity platform eventually produces one attractive customer profile.
The real test is whether Privacy, Product or Support can still understand why a consent state belongs to that person.
After the merge, can the team still identify which purpose the customer agreed to? Can it see where the decision originated? Can it explain why several identifiers were linked? If the customer later withdraws, can the organisation update the correct profile without accidentally changing another person's permissions?
Those are far better tests of identity-aware consent than simply checking whether two rows became one.
Where the consent-management layer should sit
AquaConsento’s consent-management page describes a unified consent ledger spanning web, app, API, CRM and offline journeys, with purpose-level controls and lifecycle history.
For enterprises maintaining reliable consent across customer identities and systems, the purpose of that layer should not simply be to create one master customer profile.
Its job is to keep the permission understandable while the identifiers around the customer change.
That means maintaining enough context to answer practical questions later: which person made the choice, which purpose it covered, where the event originated and why the organisation believed an identity update belonged to that customer.
For teams evaluating a consent management system in India, that is a more useful capability to examine than asking whether the software can simply consolidate customer records.
Identity resolution can tell the organisation that four IDs probably belong together.
Consent governance still has to decide what is safe to carry across that relationship.
A unified customer view should not erase the story
Meera will probably change identifiers again.
She may replace her phone. Use a different email address. Buy another device. Create another account and ask Support to merge it.
None of that should require the organisation to reinvent the history of what she chose.
A mature user consent management model accepts that customer identity is not static. Identifiers change around the person, while consent decisions continue to belong to particular purposes and moments in time.
That is the standard worth designing for.
Not a perfect customer record.
A consent history that still makes sense after the customer record changes.
Frequently Asked Questions
Should an email address be used as the unique identifier for consent?
Not automatically. A verified email can be a strong identity signal, especially when it is tied to an authenticated account, but addresses can change, be shared or eventually be reused. Consent should remain connected to the person and purpose rather than being permanently owned by one email address.
What happens to consent when a customer changes their phone number?
Where the organisation has reliably established that the new number belongs to the same customer, the current identity relationship can be updated without rewriting the historical consent event. The previous event should retain enough context to show what happened at the time.
Is a device ID the same as a customer identity?
No. A device or browser identifier describes a technical environment and may help with identity matching, but it does not necessarily identify one individual. Shared devices are a simple example of why device identity should not automatically inherit a person's consent state.
What should happen when two customer profiles are merged?
The organisation should preserve enough consent history to understand the purpose, event timing, source identity and later changes. Merging customer profiles should not automatically collapse several purpose-level consent decisions into one generic state.
How is identity resolution different from consent management?
Identity resolution determines whether several identifiers or profiles belong to the same person. Consent management records what that person chose for a particular purpose and how the decision changed over time. They need to work together, but solving identity does not automatically resolve consent.