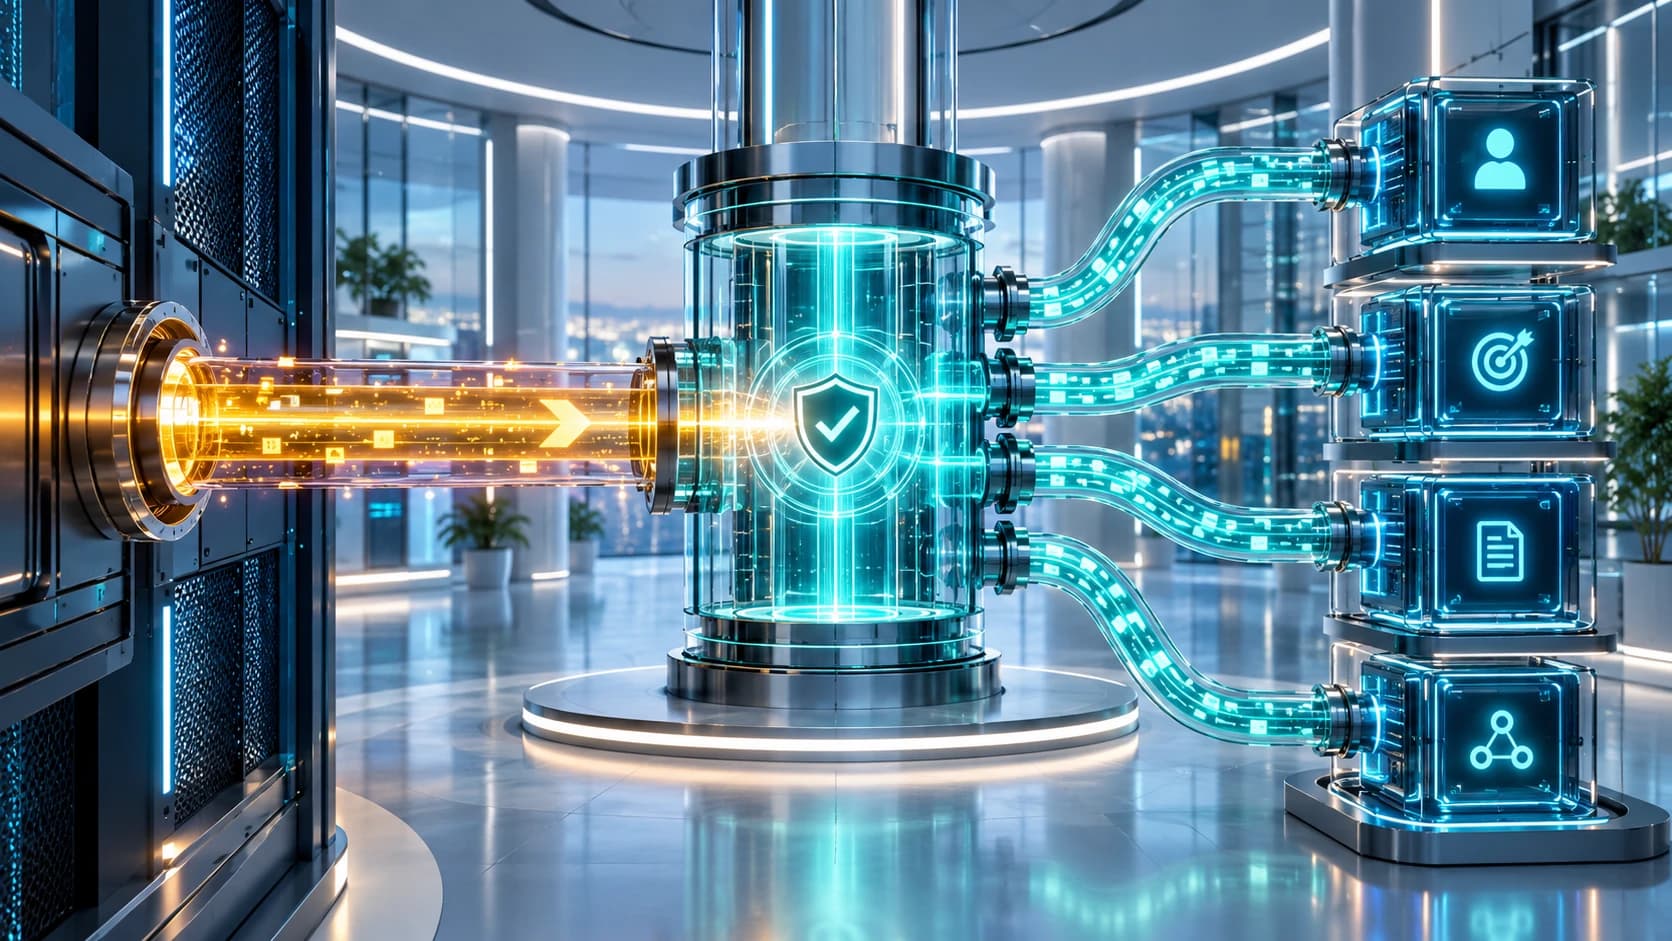
At 2:15 p.m., a customer turns off personalized offers in an app.
The preference centre updates immediately. The setting now says “Off,” exactly as the customer expects.
But the recommendation engine is still using an older profile. The CRM has its own version of the preference. A campaign workflow has not received the change yet.
From the customer’s point of view, the decision has been made.
From the enterprise’s point of view, the work has only started.
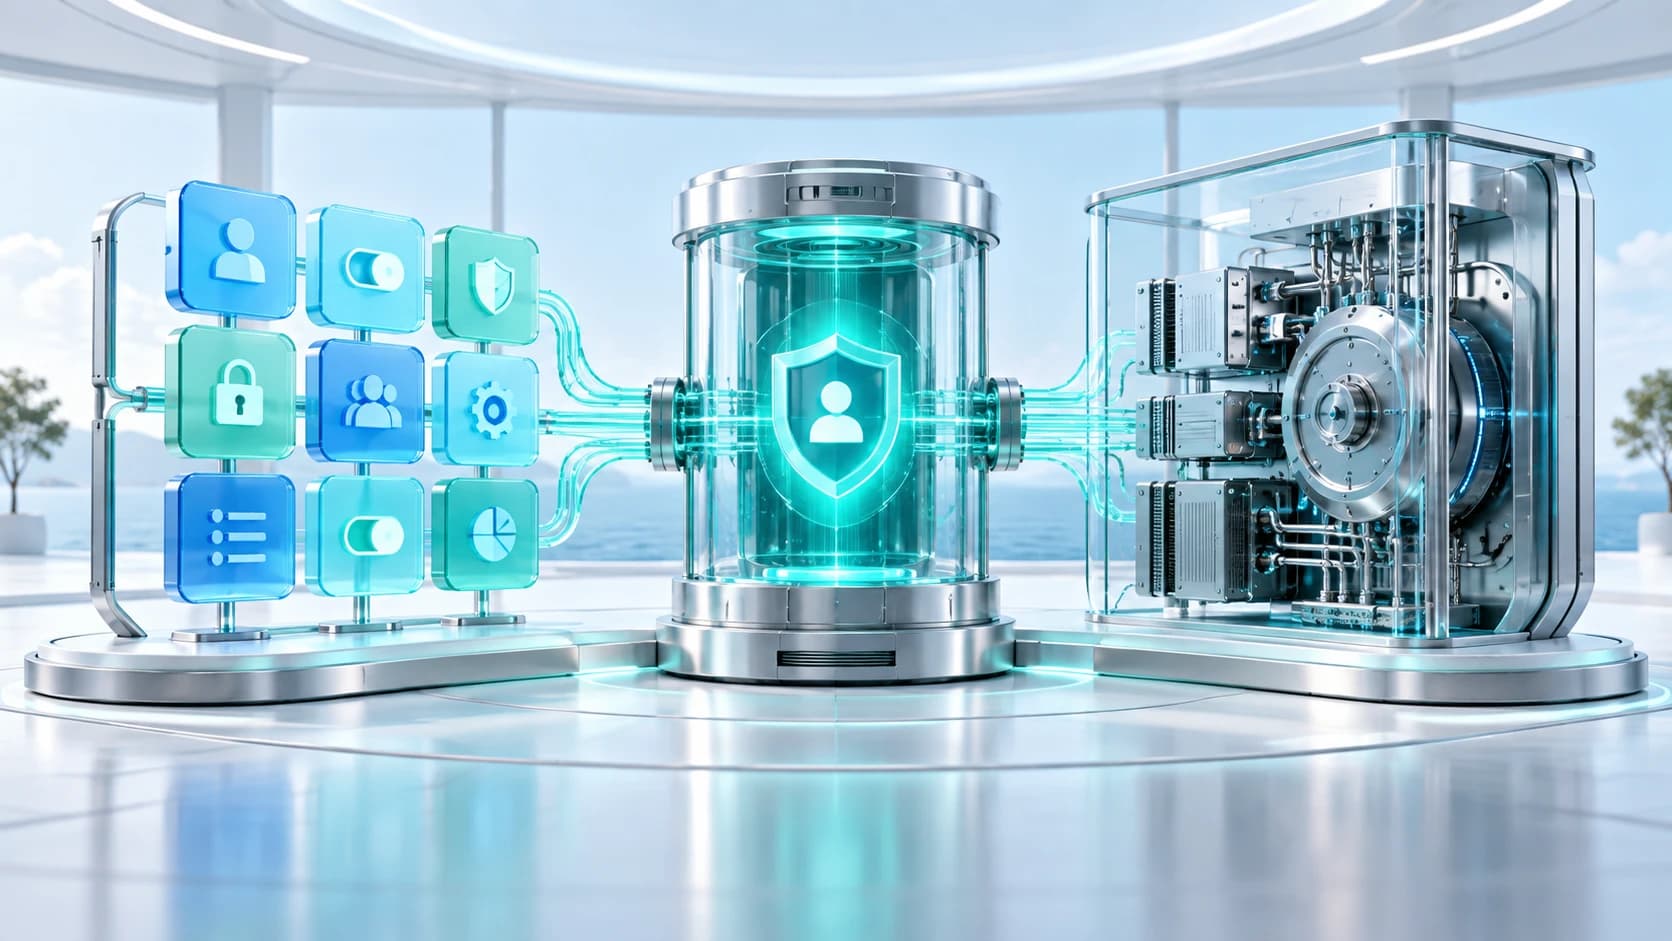
This is the distinction that matters when designing a modern consent architecture: a preference centre records and displays the user’s choice, while a policy or decision layer determines how that choice should affect actual data use across systems.
For organisations evaluating a consent management platform in India, the quality of the user interface matters. But what happens after the preference changes matters more.
A preference centre is the visible part of consent
A preference centre has a straightforward job: help people understand and manage their choices.
Depending on the business, that may include preferences for:
- marketing communications;
- personalisation;
- communication channels;
- product updates;
- specific processing purposes.
This is where consent becomes visible to the customer.
Under the Digital Personal Data Protection Act, 2023, consent must meet statutory requirements including being free, specific, informed, unconditional and unambiguous, with clear affirmative action. The Act also provides for withdrawal of consent.
The Digital Personal Data Protection Rules, 2025 add further operational detail around notices and specified purposes.
Neither the Act nor the Rules require an enterprise to build software literally called a “preference centre” or a “policy engine.” Those are implementation choices.
The legal requirement concerns consent and processing. The architecture is how an organisation makes those requirements work consistently in production.
And that is where many consent programmes become more complicated than the preference screen suggests.
A customer choice is not yet a processing decision
Suppose a customer allows service emails but declines promotional email.
The preference centre can display both choices perfectly.
Now consider the marketing system. It sees a field called:
email = true
That value alone is not enough.
It may mean the customer can still receive account updates. It does not necessarily mean the customer has agreed to promotional messages.
The same problem appears with broader labels.
A field such as:
marketing = false
may tell the business something important, but it does not automatically explain whether in-app personalisation, product recommendations or another use of customer data should also stop.
The issue is not poor software.
The issue is loss of context.
A usable consent model often needs to preserve several dimensions together: the purpose, the channel, the type of data use and the current consent state.
That context belongs behind the preference centre, where enterprise systems can interpret it consistently.
The architecture works better when each layer has a clear job
The easiest way to see the difference is to follow one consent decision through the stack.
Imagine the customer has selected:
Personalised offers: Off
At the customer-facing layer, that choice needs to be captured clearly and reflected back accurately.
Behind the interface, the organisation needs to translate the choice into something operational. The relevant context might include the purpose—product personalisation—the mobile channel, the current withdrawal state and the fact that purchase-history data is being considered for recommendations.
The resulting decision could be simple:
Do not use this customer profile for personalised offers.
The recommendation service then has to respect that result.
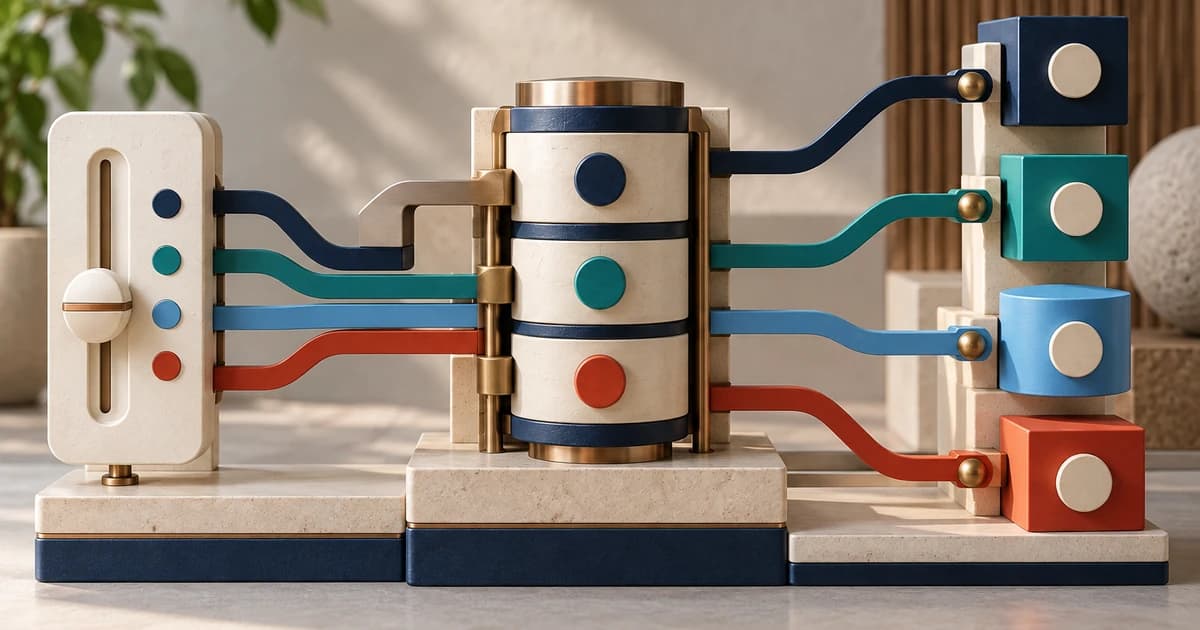
These are three different responsibilities: capturing the choice, interpreting the choice and enforcing the decision.
Keeping them separate makes the system easier to govern.
It also makes failures easier to diagnose.
If the preference centre shows the wrong value, the problem is likely in capture or state retrieval.
If the stored state is correct but the wrong decision is produced, the policy logic needs attention.
If the policy decision says “do not process” and the application continues anyway, the failure sits downstream.
That is far more useful than treating every consent problem as a generic “CMP issue.”
Purpose and channel should not become one universal switch
Consent usually becomes fragile when several different decisions are compressed into one field.
Consider this simplified example:
| Purpose | SMS | App | Relevant data use | |
|---|---|---|---|---|
| Service communication | Allowed | Allowed | Allowed | Account and service information |
| Promotional offers | Withdrawn | Withdrawn | Allowed | Contact and campaign data |
| Personalisation | N/A | N/A | Withdrawn | Behavioural/profile data |
Now reduce that entire model to:
consent = false
The implementation becomes simpler.
The meaning becomes much worse.
A customer may have withdrawn promotional email while still expecting service communication. They may reject app personalisation without changing their SMS choice.
The front end does not need to expose the underlying data model in technical language. In fact, it should not.
The customer experience should remain simple.
The backend model needs enough precision to preserve what the customer actually decided.
That is why purpose-level consent becomes important in enterprise systems. One person can have several valid, independent consent states at the same time.
Problems begin when every application interprets consent differently
A large organisation may have a website, mobile app, CRM, campaign platform, recommendation service and customer-data environment.
The customer sees one company.
The technology stack sees six systems.
If every application reads raw preference fields and applies its own interpretation, small differences start to appear.
The CRM team may understand marketing=false as “do not send promotional email.”
The mobile team may use it to disable marketing notifications.
The recommendation service may ignore it because it has a separate personalisation flag.
Each implementation can look reasonable on its own.
Together, they create inconsistent consent behaviour.
A governed policy layer reduces that risk by moving the interpretation of consent out of individual applications.
The applications still perform the actual business processing. They simply stop inventing their own definition of what the customer’s consent means.
So where should the downstream decision live?
The preference centre should not be responsible for deciding every downstream use of personal data.
Its role is customer interaction.
The better place for processing decisions is a governed backend layer that can evaluate the authoritative consent state against the actual purpose and context of the proposed data use.
That layer may be part of a larger consent platform rather than a separate standalone service. The label matters less than the responsibility.
A practical division looks like this:
| Responsibility | Preference Centre | Consent/Policy Layer | Business Application |
|---|---|---|---|
| Display the current preference | Yes | Supplies state | No |
| Capture a preference change | Yes | Records lifecycle event | No |
| Maintain authoritative purpose-level state | Reads it | Primary role | Should not create a competing truth |
| Evaluate proposed processing | No | Primary role | Requests or consumes decision |
| Perform business processing | No | No | Primary role |
| Respect allow/deny outcome | No | Produces decision | Primary role |
| Preserve consent history | Contributes event | Primary role | May add execution evidence |
This is an architecture model, not wording prescribed by the DPDP Act.
That distinction is important. A policy engine is a technical approach for making consent enforceable; it should not be presented as a statutory software requirement.
What happens after the preference changes is the real test
Return to the customer who disabled personalised offers at 2:15 p.m.
The new choice should not remain trapped in the preference-centre database.
It needs to become part of the organisation’s authoritative consent state.
Systems relying on that state then need access to the change.
Some enterprises distribute consent changes as events. Others query the latest state when an application is about to perform a governed activity. Many mature environments use both approaches.
There is no single technical design that every organisation must follow.
But one thing should always be clear: which state is authoritative when systems disagree.
That is where consent governance starts becoming meaningful.
A platform is no longer simply storing preferences. It is helping the organisation translate user choices into consistent operational behaviour.
Event-driven updates work well—until one is missed
Event-based integration is common.
When a customer changes consent, the platform sends an event to systems that need to know.
The CRM updates its record. The campaign platform changes eligibility. The recommendation service updates its local state.
This design can work very well.
It also creates the familiar problems of distributed systems: an event can arrive late, fail completely or be processed incorrectly.
If the consuming application continues using an old copy, consent has become stale.
That is why event delivery alone should not be confused with successful enforcement.
The organisation still needs visibility into whether the relevant systems actually applied the new state.
Real-time decisioning solves a different problem
Another approach is to have applications check the current consent state when processing is about to occur.
Rather than trusting a copied preference from yesterday, the application requests the current decision.
This can reduce stale-state problems.
It introduces different engineering concerns: latency, availability, resilience and what should happen when the decision service cannot be reached.
Neither approach is automatically “better.”
An enterprise may use events to keep systems synchronised and runtime checks for particularly sensitive or important data uses.
The important thing is that the design is deliberate.
If nobody can explain how a system decides whether processing is allowed, the architecture is already too ambiguous.
Keep business rules out of the preference screen
There is another failure pattern that starts innocently.
A Product team adds some logic to the preference centre because it is convenient.
One customer type needs a different option, so another rule is added.
Mobile needs slightly different behaviour, so another version appears there.
A regional requirement arrives later.
Before long, consent logic is scattered through frontend code, mobile releases, CRM automations and backend services.
Now a privacy-policy change becomes a software-release project involving several teams.
AquaConsento has explored this problem separately in its analysis of which consent changes should be manageable without repeatedly releasing application code.
The lesson is straightforward.
The preference centre should remain focused on presenting and capturing choices.
Rules governing how those choices affect downstream processing are easier to review and change when they live in a governed backend layer.
What should buyers look for in a consent management platform?
A polished preference centre is useful.
It is not enough.
For teams evaluating a consent management platform, the stronger questions appear behind the interface.
The platform should make it possible to preserve purpose-level consent states, maintain a lifecycle history and connect consent changes with the systems that depend on them.
It should also give teams a clear way to understand what happened when consent changed.
That is particularly relevant for organisations operating several customer systems under India’s DPDP framework.
A central platform for governing customer consent is most useful when it connects the customer-facing choice with governance, evidence and enterprise integrations rather than treating each application as its own source of truth.
AquaConsento’s platform architecture is positioned across capture, governance, audit/evidence and deployment/integration layers, including APIs and webhooks for enterprise workflows.
The useful buying question is therefore not simply:
Does this platform have a preference centre?
A better test is whether a preference change can travel from the customer interface to the system that actually uses the personal data.
Follow one real preference from beginning to end
There is a simple way to test the architecture.
Choose one preference already used by the business.
For example:
Use purchase history to personalise offers in the mobile app.
Change it.
Then follow what happens operationally.
Confirm that the consent record changes.
Trace how the recommendation service receives the new state.
Check what happens if it has an older cached copy.
Interrupt the integration.
Look at what the system does when the latest decision is temporarily unavailable.
Then inspect the evidence.
The organisation should be able to explain not only that the customer moved a toggle, but how that choice changed the processing that depended on it.
If all you can prove is that the screen changed, you have tested the preference centre.
You have not yet tested consent governance.
Frequently Asked Questions
Is a preference centre the same as a consent management platform?
No. A preference centre is normally the customer-facing interface used to view or change choices. A consent management platform can cover a broader lifecycle including consent capture, purpose-level state, withdrawals, governance, audit evidence and downstream integrations.
Does the DPDP Act require a consent policy engine?
No. The DPDP Act does not prescribe a technical component called a “consent policy engine.” It is an architectural approach that can help enterprises translate consent state into consistent downstream processing decisions.
Should downstream applications keep their own copy of consent?
They may, depending on performance, resilience and architecture requirements. The more important question is whether the organisation has a clearly defined authoritative state and can prevent an outdated local copy from overriding a newer customer decision.
Should the policy layer perform the business processing?
Usually no. The policy layer evaluates the consent state and processing context. The business application remains responsible for performing—or not performing—the actual processing.
Why does this matter for a consent management platform in India?
Because one customer choice may affect several applications, purposes and channels. A well-designed consent architecture helps those systems interpret the choice consistently while preserving a clear record of how consent changed over time.
The preference centre is where the customer sees consent. The real work happens behind it.
A preference centre should be simple.
Customers should be able to understand their choices, change them without friction and trust that the organisation will respect the result.
They should not need to know how a policy engine works.
That complexity belongs inside the enterprise.
The consent platform needs to preserve what the customer decided. The decision layer needs to interpret that choice consistently. The downstream system needs to behave accordingly.
When those three parts stay aligned, a preference change becomes more than a UI update.
It becomes an enforceable change in how the organisation uses data.
For teams evaluating a consent management platform, that is the architecture worth testing.